Ever thought of why regulators require penetration testing?
For many organisations, a penetration test begins with a requirement: A regulator asks for it; an auditor recommends it; a customer includes it in a contract.
The result is often the same. The organisation runs the test, reviews the report, fixes the findings, and moves on until the next assessment. What is often overlooked is a more important question: Why do regulators place so much emphasis on penetration testing in the first place?
The answer is surprisingly simple. Regulators are not interested in whether an organisation owns security tools. They want evidence that those controls actually work when faced with a genuine attack. A penetration test provides that evidence.
Security Controls Look Good on Paper. Reality Is Different.
Most organisations invest heavily in cybersecurity. They deploy firewalls, endpoint protection, multi-factor authentication, monitoring platforms and access controls. They create policies, conduct training and complete audits. All of these measures are important however, regulators understand something that experienced security professionals have known for years: A control that exists is not necessarily a control that works.
A firewall may be incorrectly configured, an application may contain a flaw that bypasses authentication, an employee account may have excessive privileges, a critical system may never have been reviewed after years of upgrades and changes… Penetration testing helps uncover these practical weaknesses before an attacker discovers them.
Why Regulators Value Penetration Testing
Unlike questionnaires, audits and policy reviews, a penetration test evaluates security controls under realistic attack conditions. It answers questions such as:
- Can an attacker gain access to sensitive information?
- Can a low-privileged user escalate their privileges?
- Can a weakness in a web application lead to a wider compromise?
- Can an attacker move through the internal network if they gain an initial foothold?
These are the same questions regulators ask when considering operational resilience and cyber risk. Penetration testing provides an independent assessment of how exposed an organisation really is.
Real Examples of Regulatory Expectations
DORA (European Union)
The Digital Operational Resilience Act (DORA) requires financial entities to regularly test their digital operational resilience. DORA specifically includes penetration testing as part of its resilience testing framework and requires certain higher-risk financial entities to perform advanced Threat-Led Penetration Testing (TLPT) exercises.
The reason is clear: European regulators recognise that cyber resilience cannot be measured by policies alone. Organisations must demonstrate that critical systems can withstand realistic attacks and that weaknesses can be identified before they result in disruption.
PCI DSS
The Payment Card Industry Data Security Standard (PCI DSS) requires organisations that process, store or transmit payment card data to perform both internal and external penetration testing on a regular basis and after significant changes.
Organisations handling payment card information represent attractive targets for cybercriminals. PCI DSS recognises that vulnerability scans alone cannot demonstrate whether attackers can exploit weaknesses and gain access to cardholder data. Penetration testing provides assurance that security controls are genuinely effective.
TIBER-EU
The European Central Bank developed the TIBER-EU framework to help financial institutions assess resilience against sophisticated and realistic attacks. Rather than simply identifying vulnerabilities, TIBER-style testing evaluates whether organisations can detect, respond to and recover from attacks that mirror real-world threats.
This reflects an important shift in regulatory thinking. The question is no longer: “Can attackers get in?”. The question is: “How quickly can the organisation detect, contain and recover from the attack?”
What Customers Gain from Regular Penetration Testing
The value of penetration esting extends far beyond compliance. Customers and business partners increasingly want assurance that the organisations they rely on take cybersecurity seriously. A recent penetration test provides evidence that:
- Security controls are being independently reviewed.
- Vulnerabilities are being actively identified and remediated.
- The organisation is committed to continuous improvement.
- Cybersecurity risks are being managed proactively rather than reactively.
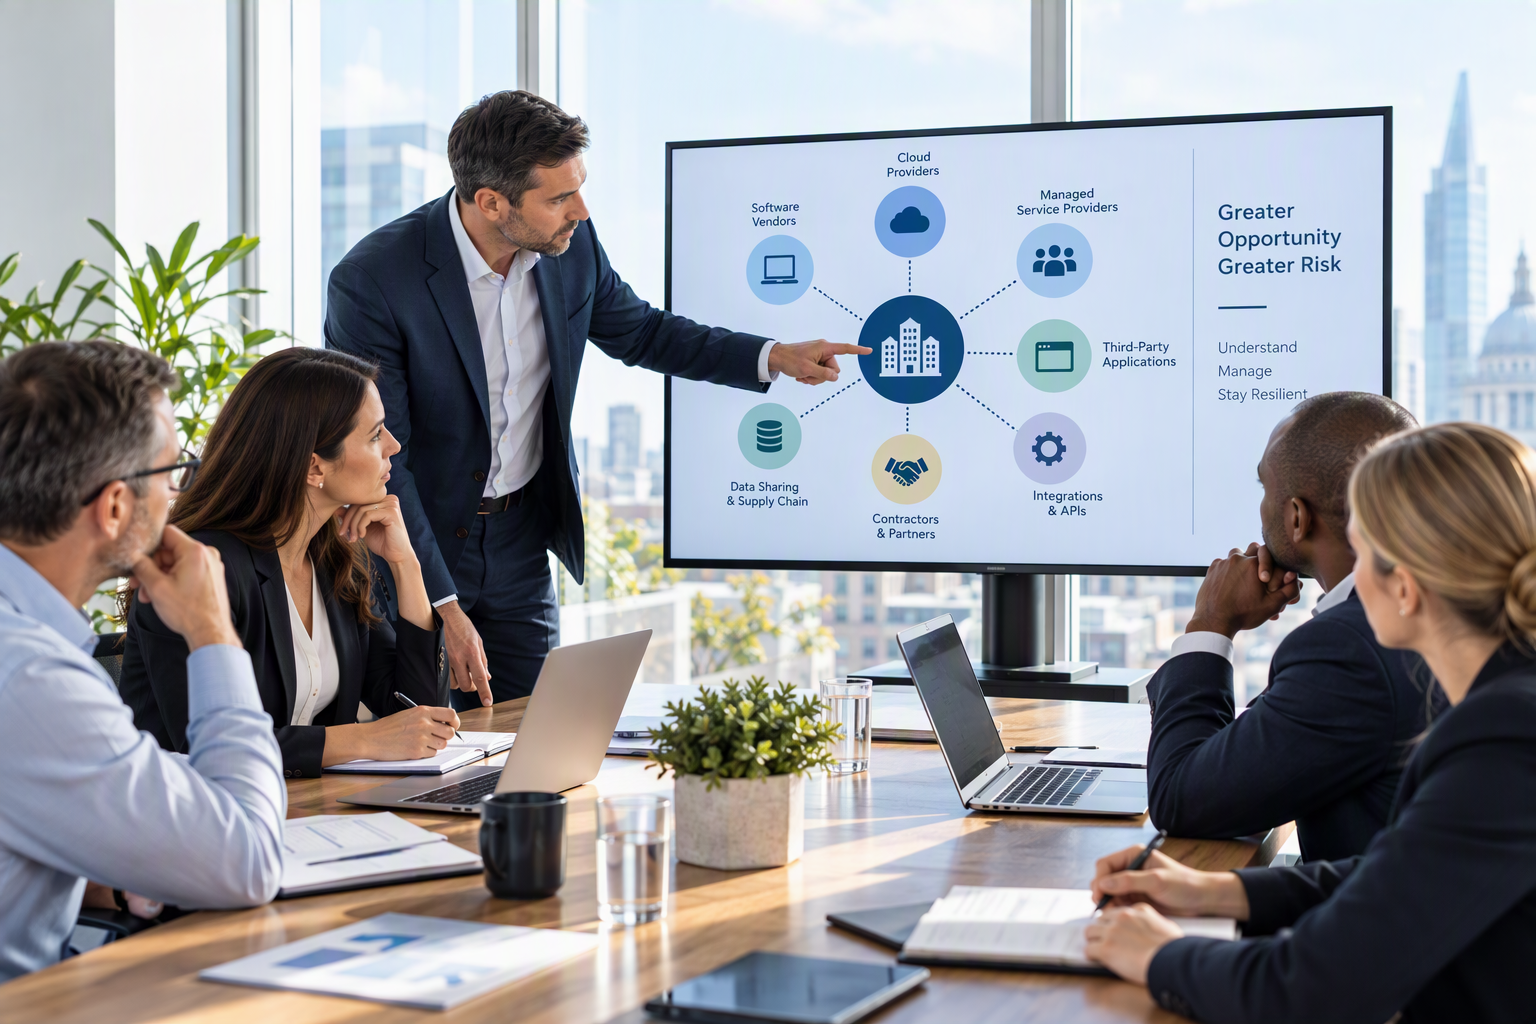
In a world where supply chain attacks continue to increase, this level of assurance matters.
What Regulators Gain from Penetration Testing
From a regulatory perspective, penetration testing provides confidence in several areas. It demonstrates:
- Active security governance.
- Ongoing risk management.
- Independent validation of security controls.
- Commitment to operational resilience.
- A proactive approach to cyber risk reduction.
Most importantly, it provides evidence rather than assumptions. Regulators understand that organisations can unknowingly develop gaps between their documented controls and their actual security posture. Penetration testing helps close that gap.
The Most Important Lesson
The organisations that benefit most from penetration testing are rarely the ones that view it as a compliance obligation. They are the organisations that treat it as a business assurance exercise. After all, regulators are not mandating penetration testing simply to create more paperwork. They are asking organisations to verify something fundamental: When a real attacker arrives, will your security controls perform as expected? That is the question a penetration test is designed to answer. And that is why regulators continue to place so much value on regular testing.
In Summary
Penetration testing has become a cornerstone of modern regulatory frameworks because it provides something few other security activities can deliver: evidence. Frameworks such as DORA, PCI DSS and TIBER-EU all recognise that cybersecurity cannot be measured solely through policies, audits or technology investments. Real assurance comes from testing controls against realistic attack scenarios and understanding how an organisation performs under pressure. For regulators, that evidence supports resilience. Customer feel that it builds trust. For organisations, it provides the clarity needed to strengthen security before a cybercriminal finds the weakness first.