-
The Vulnerability Nobody Patches: How Familiarity Creates Cyber Risk
Organisations often spend years improving their security, yet some of the most dangerous vulnerabilities remain hidden in plain sight. Discover how familiarity creates cyber risk and why…
-
Security Drift: The Hidden Cybersecurity Risk Created by Everyday Change
Most cybersecurity incidents are not caused by a single catastrophic mistake. They emerge gradually as systems, users, integrations, and processes change over time. This silent phenomenon, known…
-
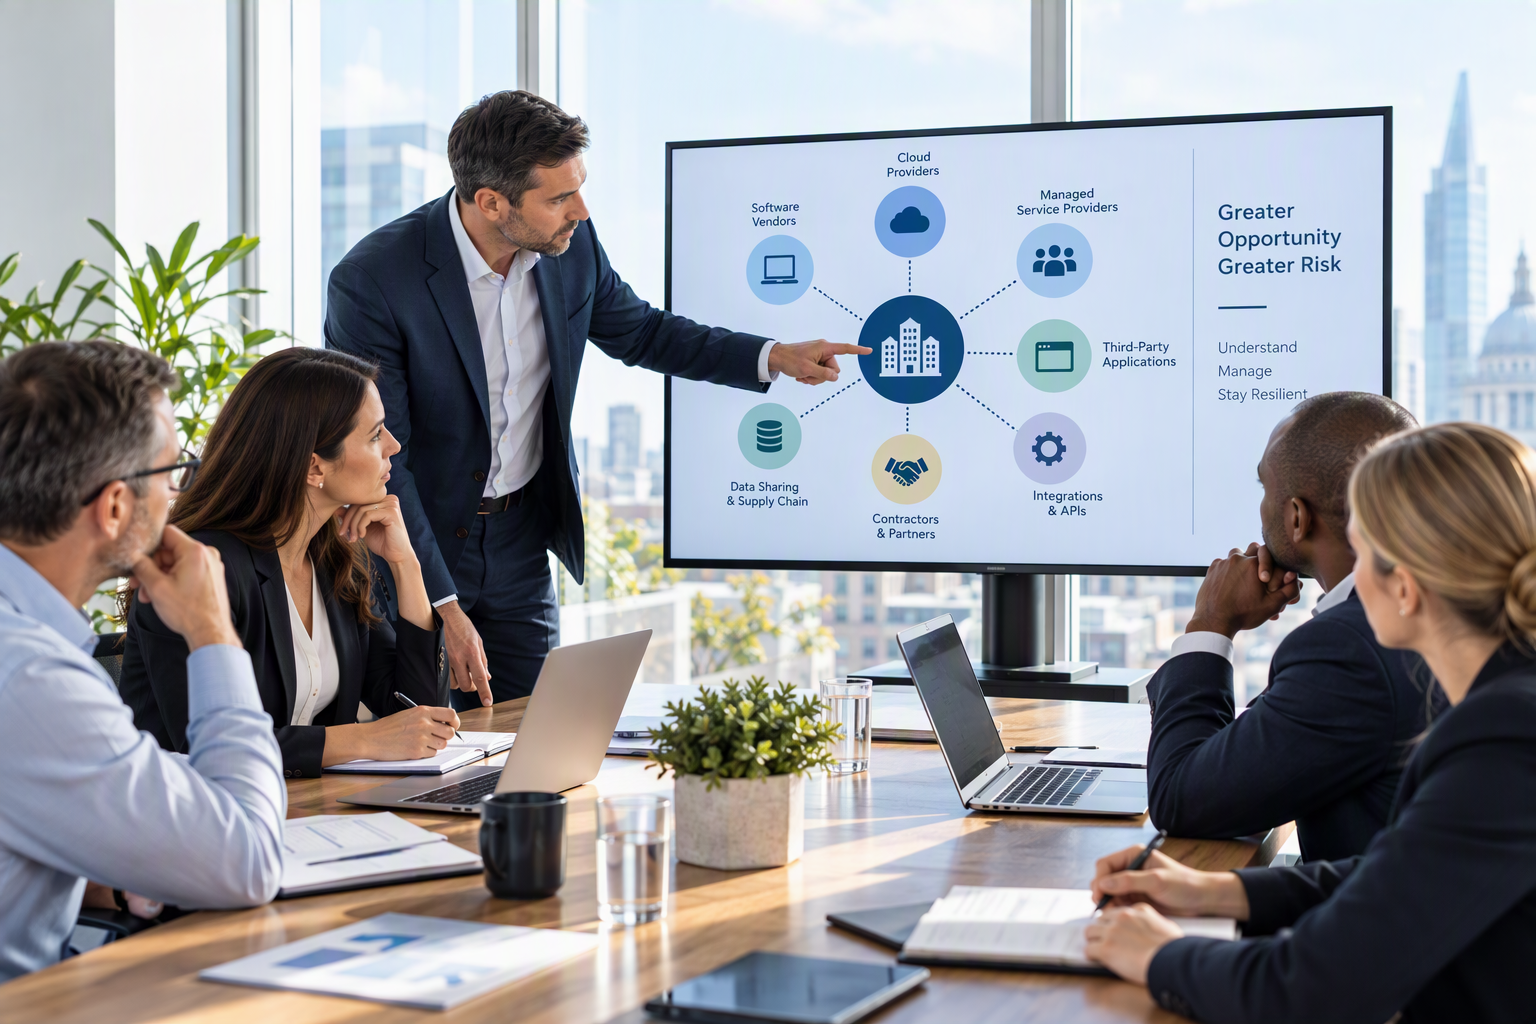
The Risk You Inherited: How Third-Party Software Is Quietly Expanding Your Attack Surface
Every new software platform, integration and supplier connection expands your attack surface. Discover why third-party cybersecurity risk is becoming one of the most important business risks organisations…
-
I’m Thinking About Planning a Penetration Test Next Year. What Do I Need to Know Now?
Many organisations know they should carry out a penetration test but leave planning until the last moment. Discover the practical steps that will help you budget correctly,…
-
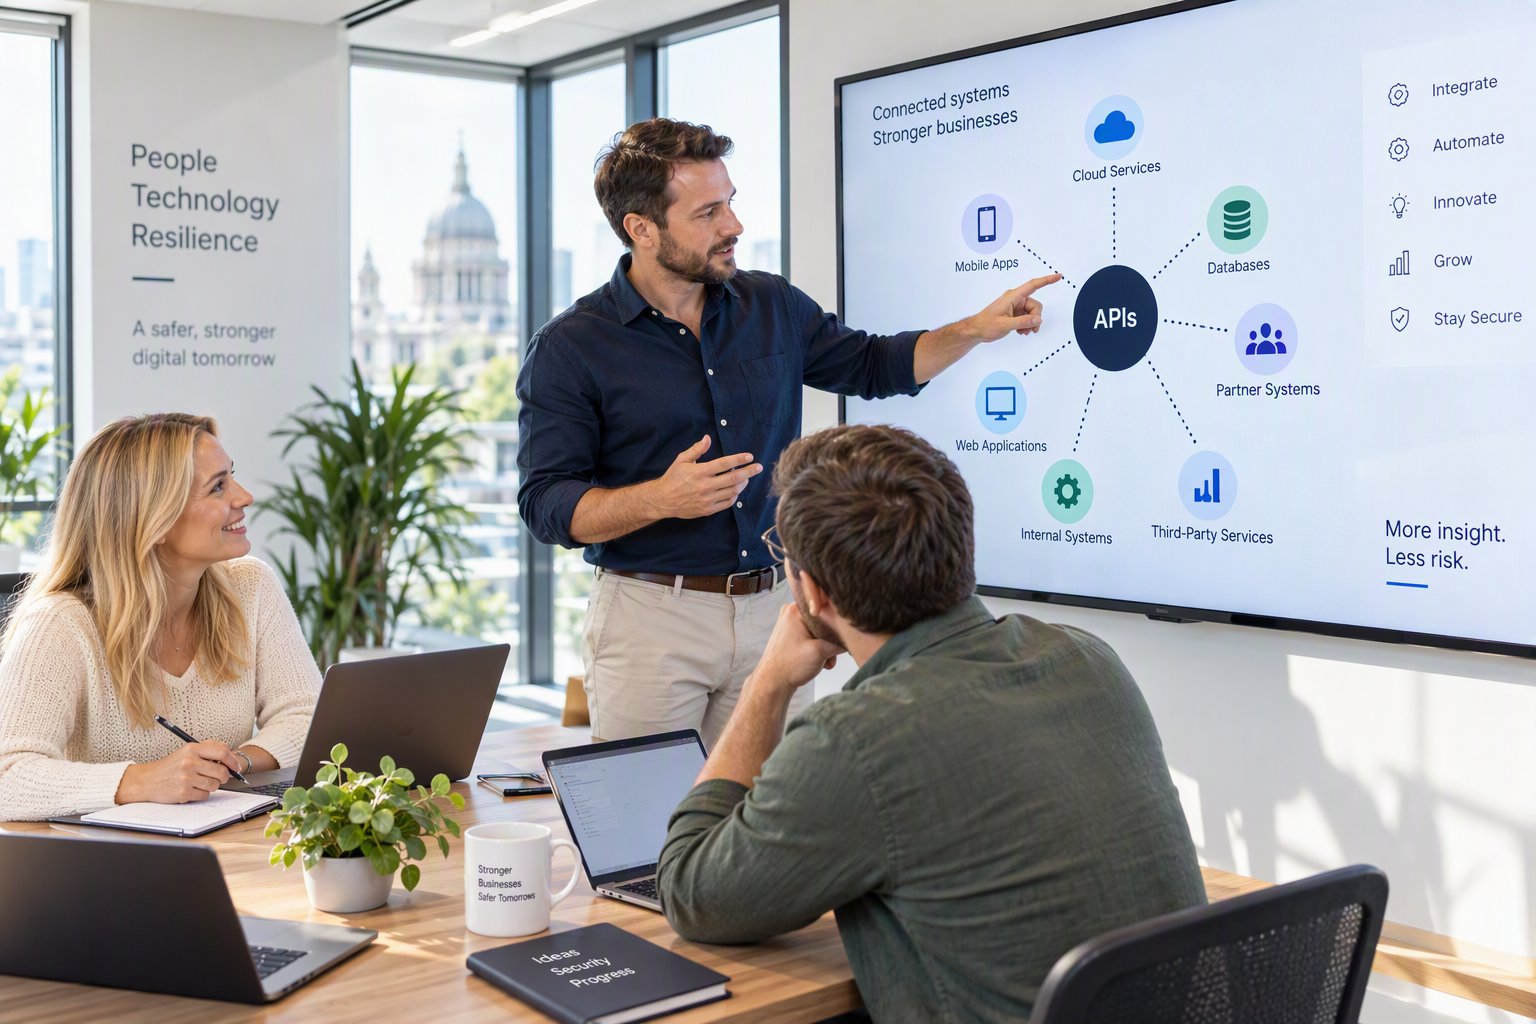
Your Business Has More APIs Than You Think. That’s Why Attackers Love Them.
Most modern businesses rely on APIs every day, often without realising it. As organisations connect more systems and services, APIs are becoming one of the most attractive…
-
Your Next Supplier Could Be Your Next Security Incident
A new supplier can bring efficiency, innovation and growth. It can also introduce cyber risk. Discover why third-party cybersecurity risk is becoming one of the most overlooked…
-
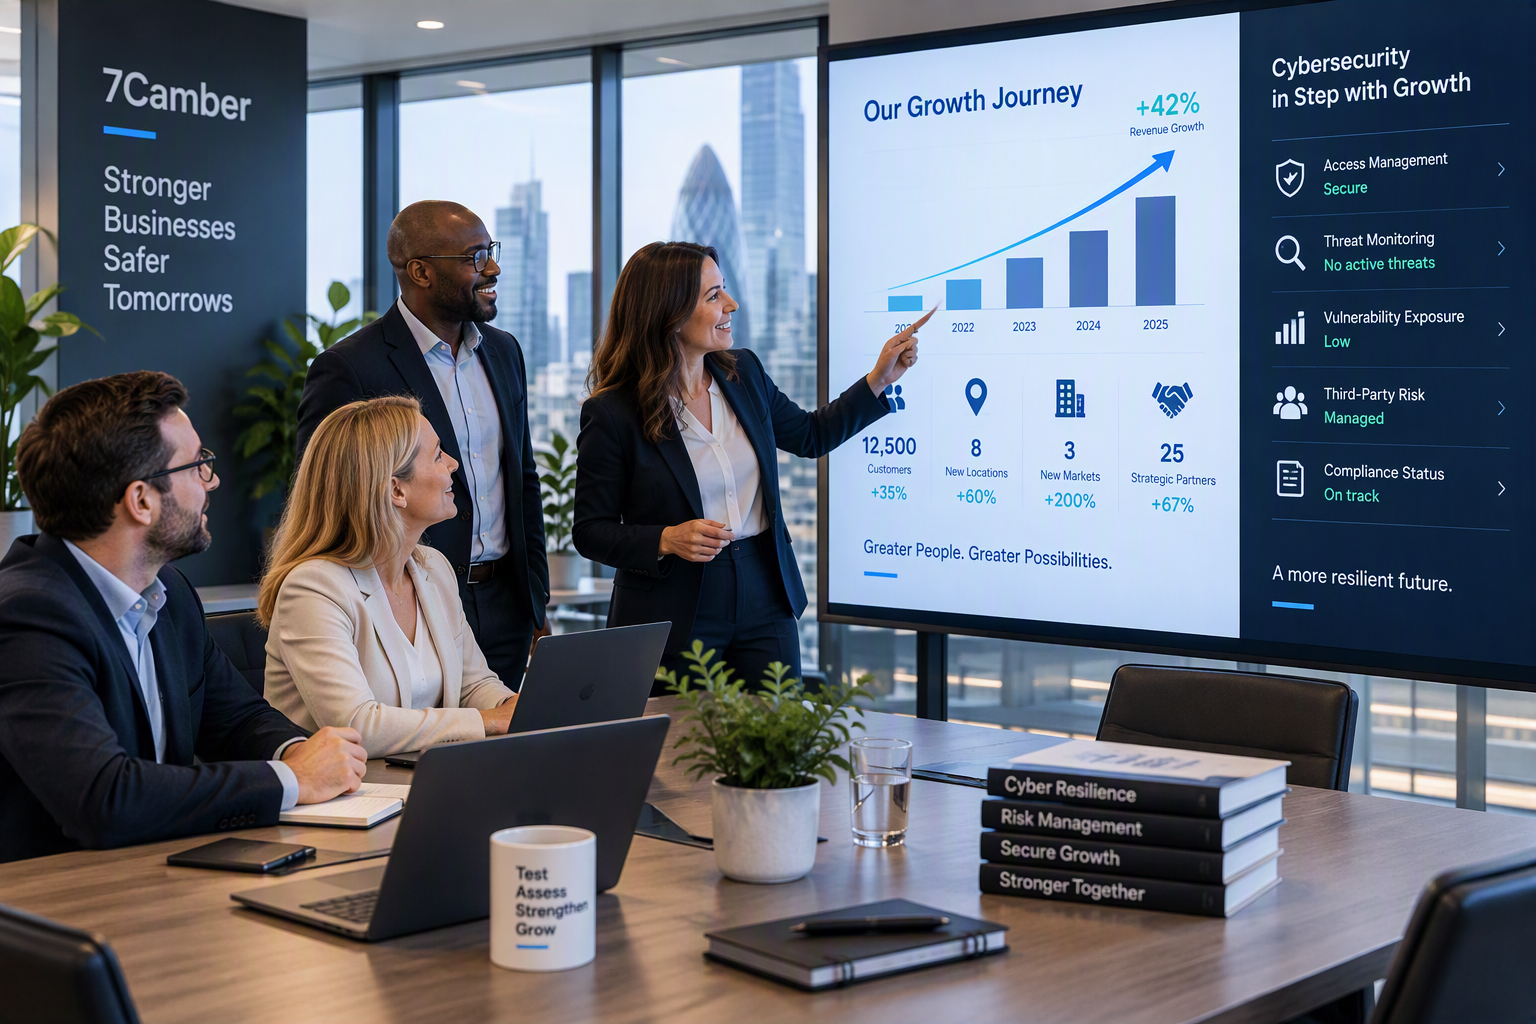
Your Next Cyber Incident Might Start During Your Best Year Ever
Cybersecurity risks do not only emerge during difficult times. In many cases, an organisation’s greatest vulnerabilities appear during periods of rapid growth. Learn why expansion, success, and…
-
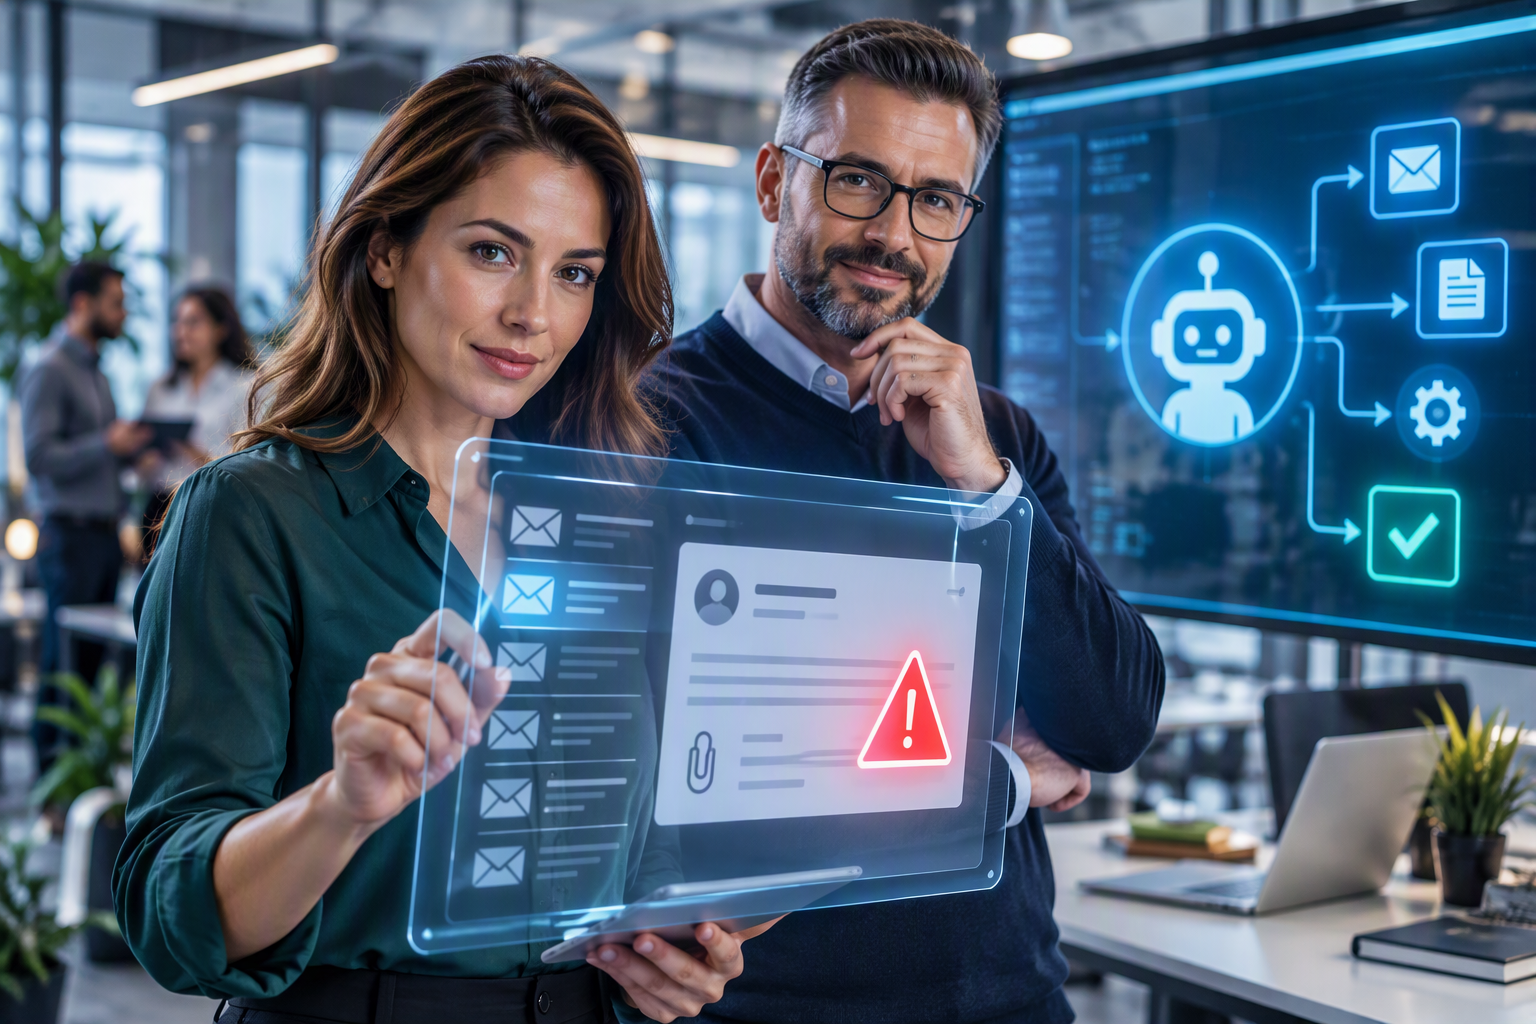
Your New Employee Never Sleeps. It Never Takes a Day Off. Can It Be Phished?
As businesses increasingly rely on AI assistants to process emails, analyse data and automate decisions, a new cybersecurity question emerges: if humans can be tricked by phishing…
-
Why Regulators Require Penetration Testing: What They See That Many Organisations Miss
Many organisations view penetration testing as a compliance exercise. Regulators see it differently. They view regular penetration testing as one of the few ways to independently verify…
-
We’ve Been Using It for Years. Surely It’s Secure by Now?
Many organisations assume that systems which have been running for years are inherently safe. Unfortunately, familiarity does not equal security. This article explores why older systems often…
-
We Merged Two Companies Successfully. So Why Did Our Cyber Risk Double?
When two companies merge, IT systems, users, applications, and data are combined at speed. While commercial integration often receives most of the attention, cybersecurity risks can be…
-
We’ve Never Had a Security Incident, So Why Would We Need a Penetration Test?
Many organisations believe they are secure simply because they have never suffered a known cyber incident. In reality, the absence of evidence is not evidence of security.…
-
We Have Cyber Insurance, So We’re Covered… Right?
Cyber insurance can help organisations recover financially after a cyber incident, but it cannot prevent attacks from happening. Discover why relying solely on insurance may leave your…
-
The Hidden Cost of Waiting: The Best Time to Run a Penetration Test Is Before the Hacker Does
Many organisations only think about penetration testing after a cyber incident. By then, the damage may already be done. Learn why preventive penetration testing helps organisations reduce…
-
The Hidden Message in the EU Cybersecurity Audit: Why Penetration Testing Matters More Than Ever
A recent European Court of Auditors report highlights growing cybersecurity challenges across Europe, including detection gaps, incident under-reporting and increasing threats. While focused on the EU ecosystem,…
-
Privilege Escalation Vulnerabilities: The Hidden Risk That Can Turn a Minor Breach into a Major Incident
Many organisations focus on preventing cyber attacks but overlook the weaknesses that allow attackers to gain greater access after a breach. Learn why privilege escalation vulnerabilities pose…
-
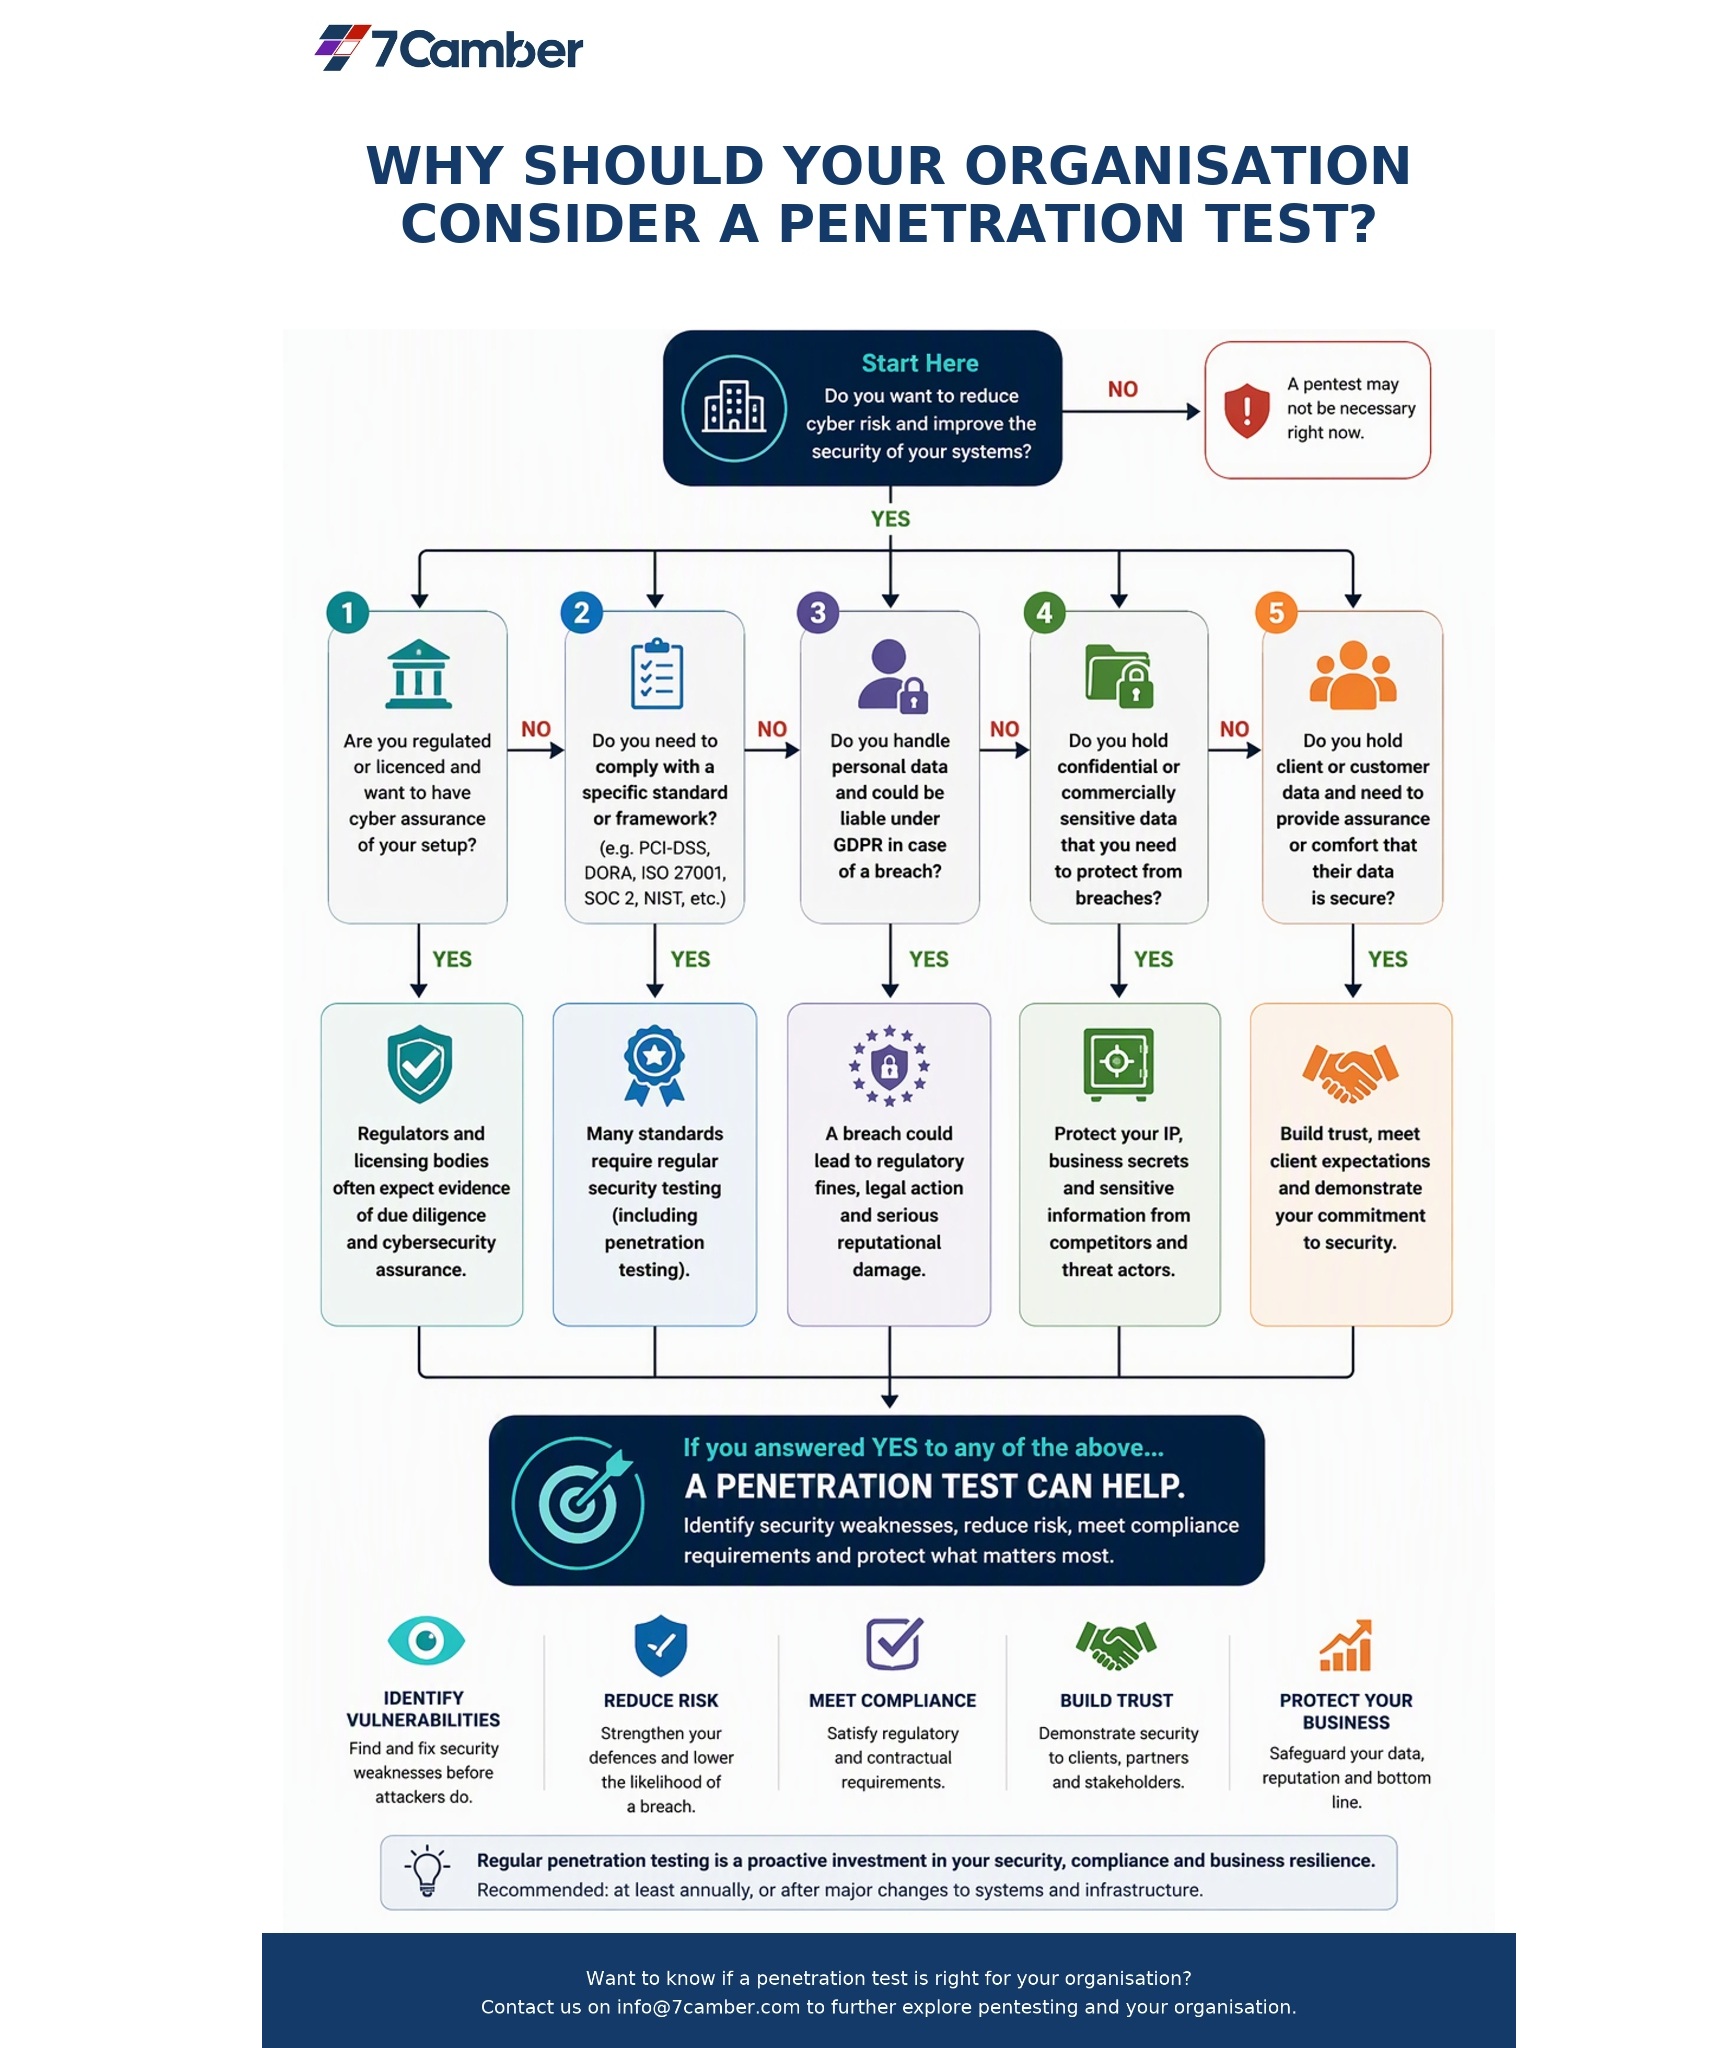
Why should I consider a penetration test?
If your organisation handles sensitive data, operates in a regulated industry, or wants to reduce cyber risk, a penetration test could be one of the smartest investments…
-
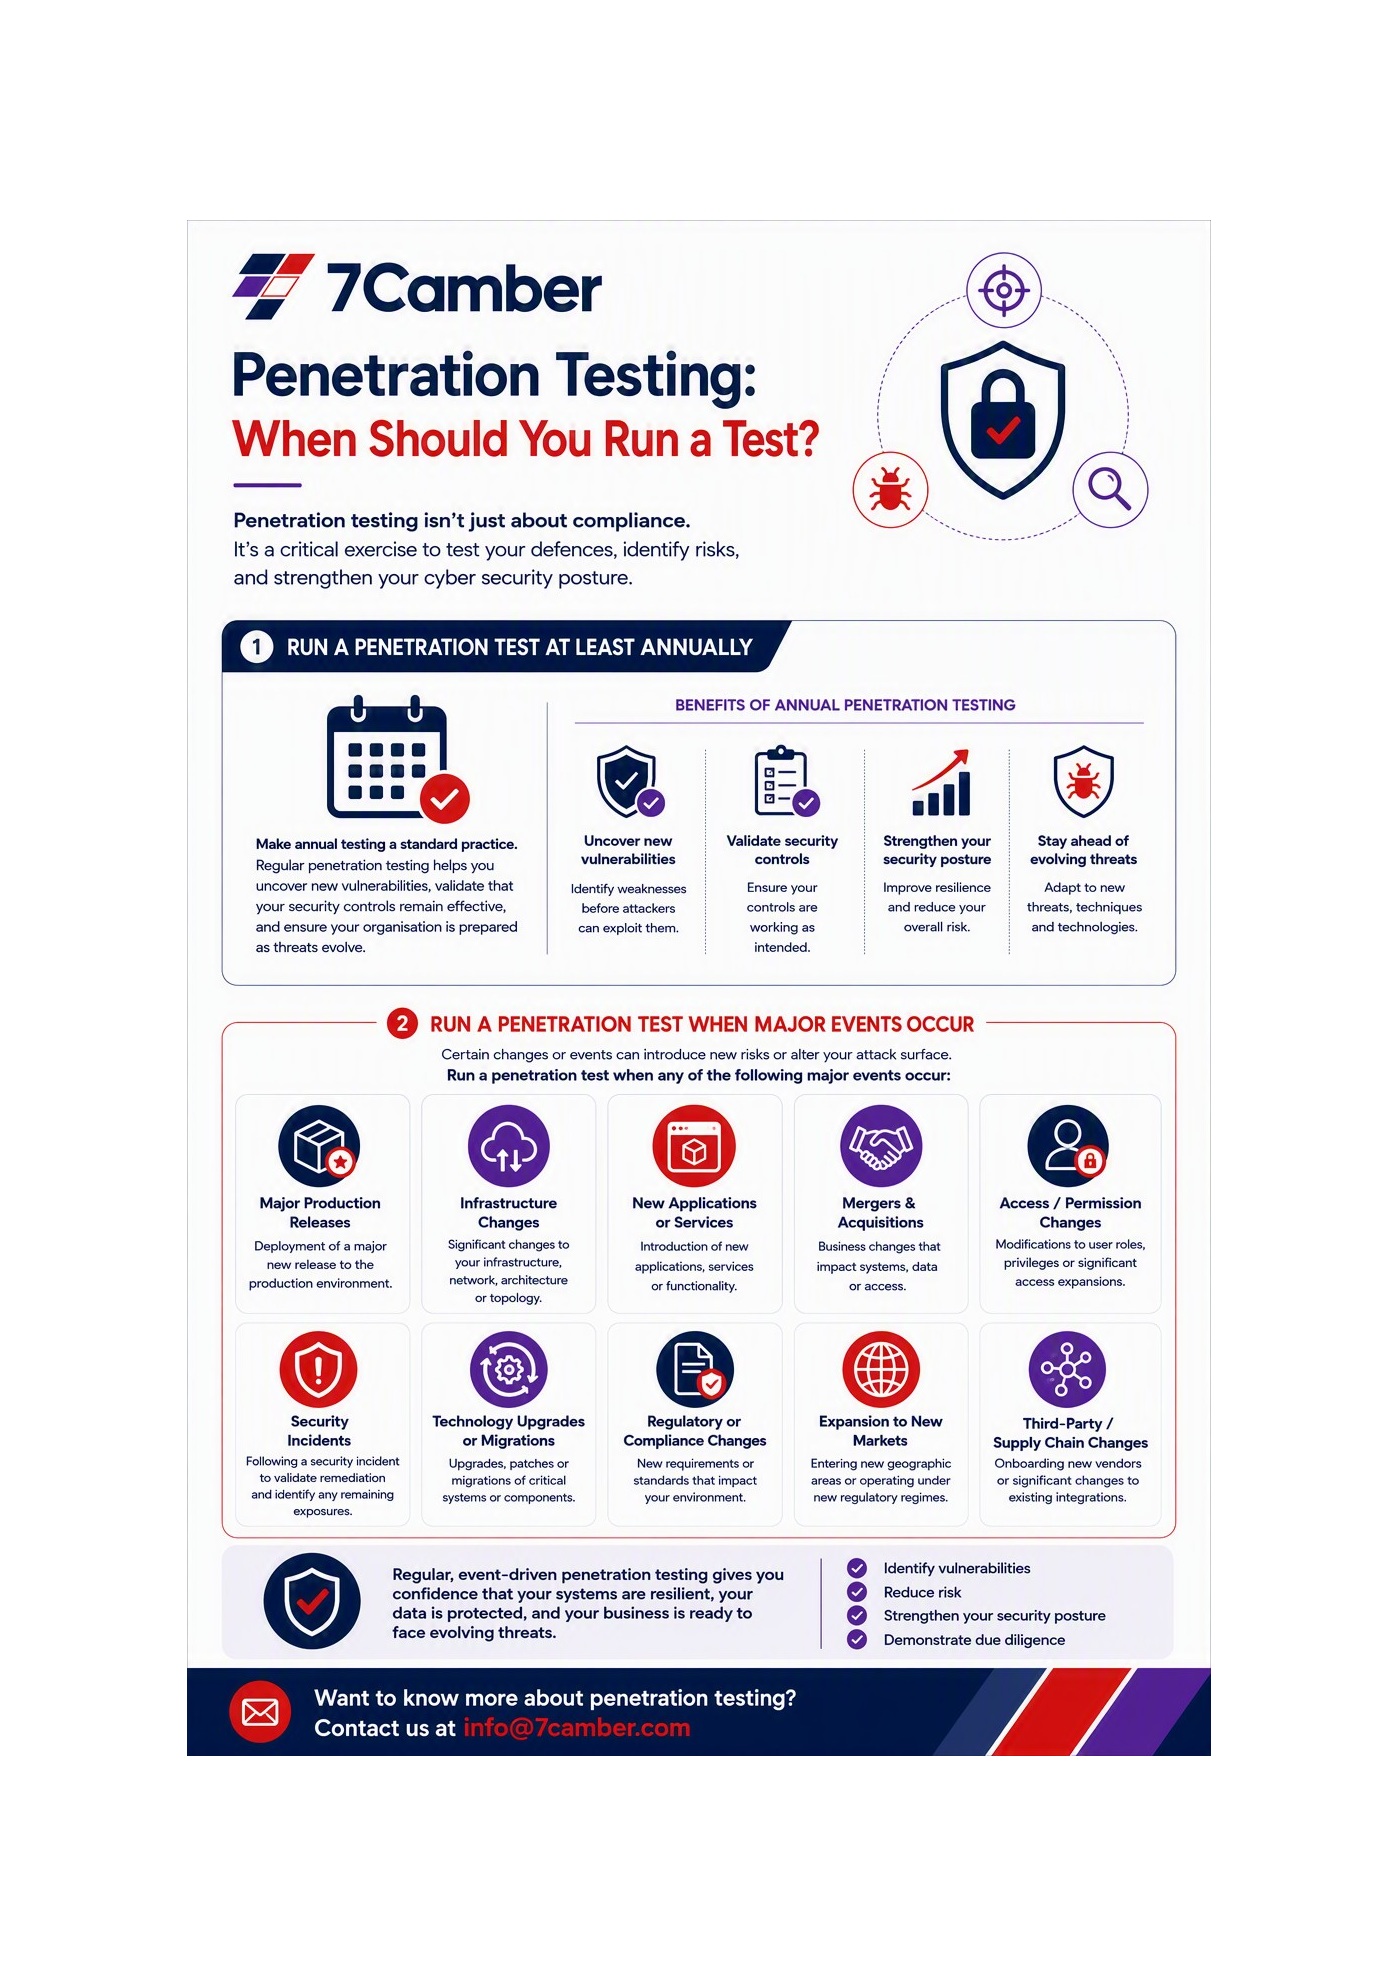
When Should You Run a Penetration Test? The Critical Moments Most Organisations Overlook
Many organisations only perform penetration tests to meet compliance requirements. However, the right time to run a penetration test is often when significant business or technology changes…
-
Beyond the Hack: Why Regulatory Insight Matters in Penetration Testing
Most penetration testing firms can find vulnerabilities. Few understand what regulators expect. Learn how 7Camber bridges that gap to deliver security testing that truly protects and prepares…
-
The Myth of Invisibility: Why “No Public-Facing Services” Is Not a Security Strategy
Having no public-facing systems doesn’t make your organisation secure. In today’s interconnected world, risk lies in access, identity, and internal complexity; making penetration testing more relevant than…

