The Risk You Inherited: How Third-Party Software Is Quietly Expanding Your Attack Surface
Most business leaders spend considerable time evaluating the risks they create themselves. They assess internal processes, review access controls and manage compliance obligations. They also invest in cybersecurity measures designed to protect their organisation from attack. Third-party cybersecurity risk creates many of the most significant risks facing organisations today.
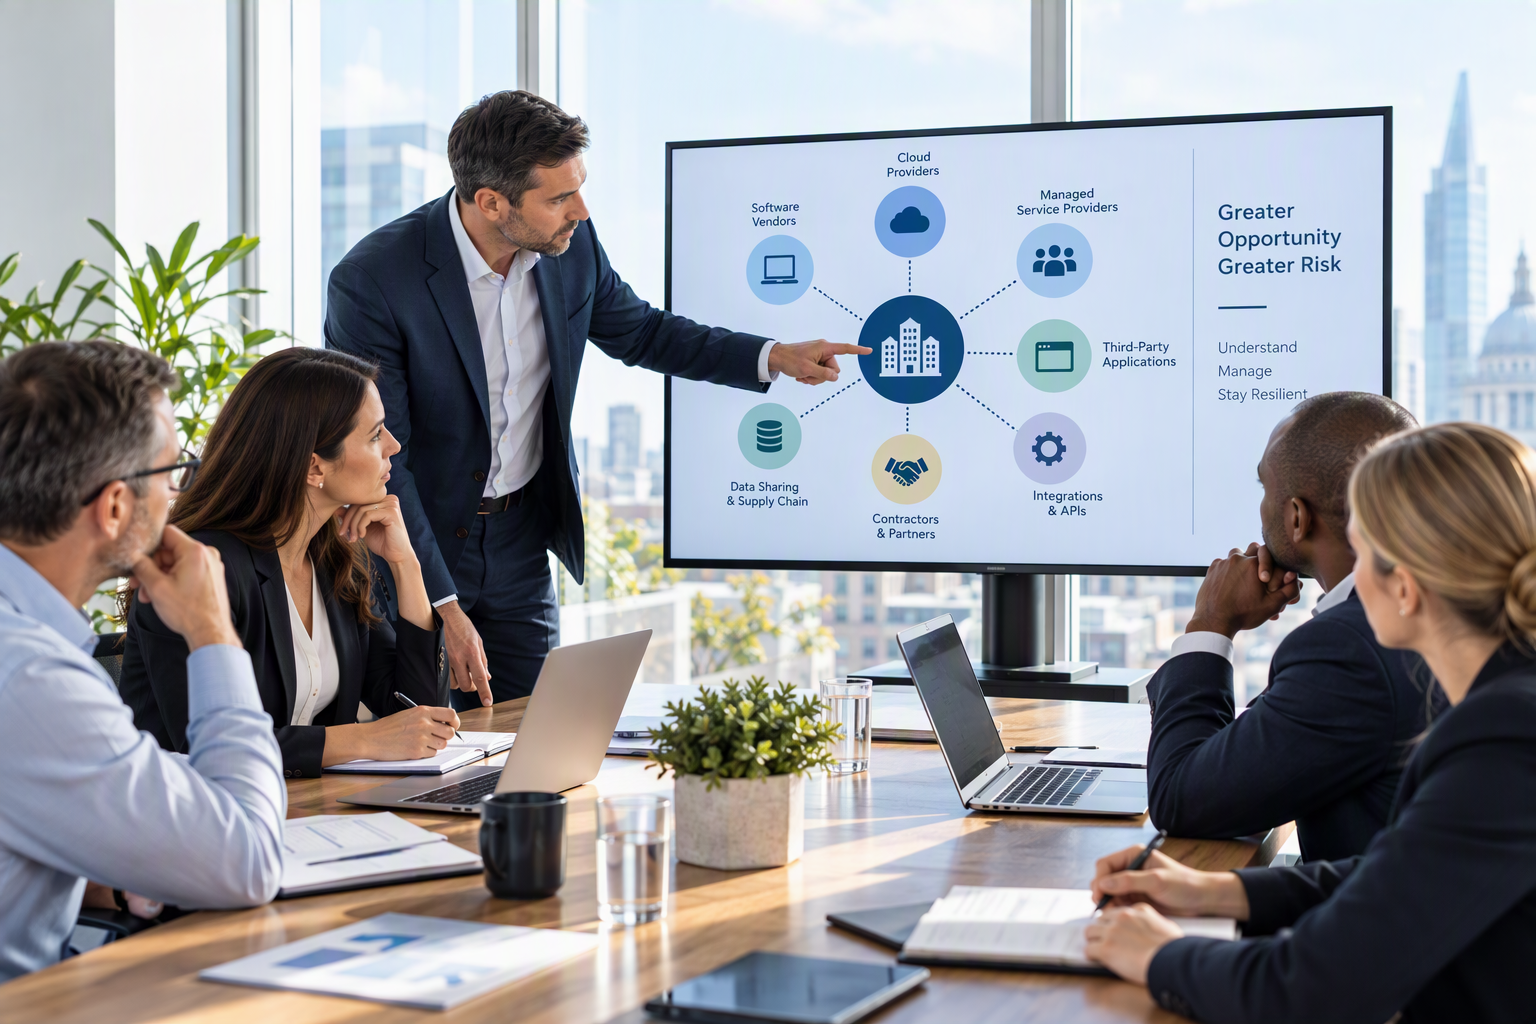
Modern businesses rely on an ever-growing ecosystem of software vendors, cloud platforms, integrations, plugins, APIs, managed service providers, and outsourced technology partners. These tools improve efficiency, support growth, and enable innovation. Over time, organisations embed these systems into their daily operations and treat them as trusted parts of the business. Unfortunately, attackers often view them differently.
Why Could Third-Party Software Be an Issue?
Every third-party application connected to your environment creates a new pathway into your organisation. While your internal security controls may be strong, a weakness within a supplier’s software, a vulnerable integration, or a poorly configured cloud service can introduce risks that sit entirely outside your direct control. This challenge is becoming increasingly difficult to manage because many organisations underestimate the scale of their third-party exposure.
A business may believe it uses only a handful of critical systems. Closer review, however, often reveals dozens or even hundreds of external applications with access to company data, employee accounts, customer information, or business processes. Over time, these connections accumulate. Organisations adopt new software, add integrations, and retain legacy systems long after their original purpose has faded from view.
The result is a growing attack surface that few organisations fully understand.
When cybersecurity incidents occur, the initial compromise is not always caused by a sophisticated attack against the organisation itself. In many cases, attackers identify a weakness elsewhere in the supply chain and use that trust relationship as an entry point. A vulnerable software update, a compromised supplier account, or an insecure integration can provide access that would otherwise be difficult to obtain. This is why understanding your third-party ecosystem is becoming just as important as protecting your own infrastructure.
Effective risk management now extends beyond firewalls, endpoint protection, and vulnerability scanning. Organisations need visibility over which suppliers have access to their systems. They need to be aware of what data is being shared, how integrations are secured, and whether third parties are maintaining appropriate cybersecurity standards. This does not mean businesses should avoid innovation or stop adopting new technology. Quite the opposite.
Looking ahead…
The organisations that gain the greatest value from digital transformation are often those that embrace new technologies confidently. They are those that understand the risks involved and have processes in place to manage them. The objective is not to eliminate third-party risk: That is impossible. The objective is to identify it, understand it, and ensure it remains within acceptable levels.
At 7Camber, we regularly encounter organisations that have invested heavily in securing their own environments while having limited visibility into the risks introduced through suppliers, business applications, APIs, and connected platforms. Security assessments frequently reveal forgotten integrations, excessive permissions, exposed interfaces, and inherited vulnerabilities that would otherwise remain unnoticed.
The reality is simple: You cannot secure only what you own. You must also understand what you trust.
As organisations continue to expand their digital ecosystems, the businesses that succeed will be those that treat third-party cybersecurity risk as a board-level business issue rather than a purely technical concern. Because the next major cybersecurity incident may not begin within your organisation at all. It may begin with a system you inherited.