Business Change
Most organisations do not wake up one morning and decide to become less secure. Yet that is exactly what happens. Not because somebody ignored security. Not because a firewall failed. Not because hackers suddenly became smarter. It happens because businesses change. This is security drift.
A new cloud application is introduced to improve productivity. An external supplier is given access to support a project. A temporary user account remains active after a contractor leaves. A business-critical API is connected to another platform. A legacy server stays online because nobody wants to risk disrupting operations.
Each decision makes perfect sense in isolation. Each change solves a genuine business problem. But over time, these small adjustments accumulate and create something many organisations never see coming: security drift.
What Is Security Drift?
Security drift occurs when an organisation’s technology environment gradually moves away from its original secure design. The controls that once protected the business are still present. Policies may still exist. Security tools may still be running. However, the environment has evolved.
New systems have been added. Staff responsibilities have changed. Suppliers have gained access. Applications have become interconnected. Cloud services have expanded. Business priorities have shifted. The result is that the security posture that existed two years ago may bear little resemblance to the environment that exists today.
Ironically, many organisations remain confident because they remember the results of a security assessment that was performed when the environment looked very different.
The Business Expansion Trap
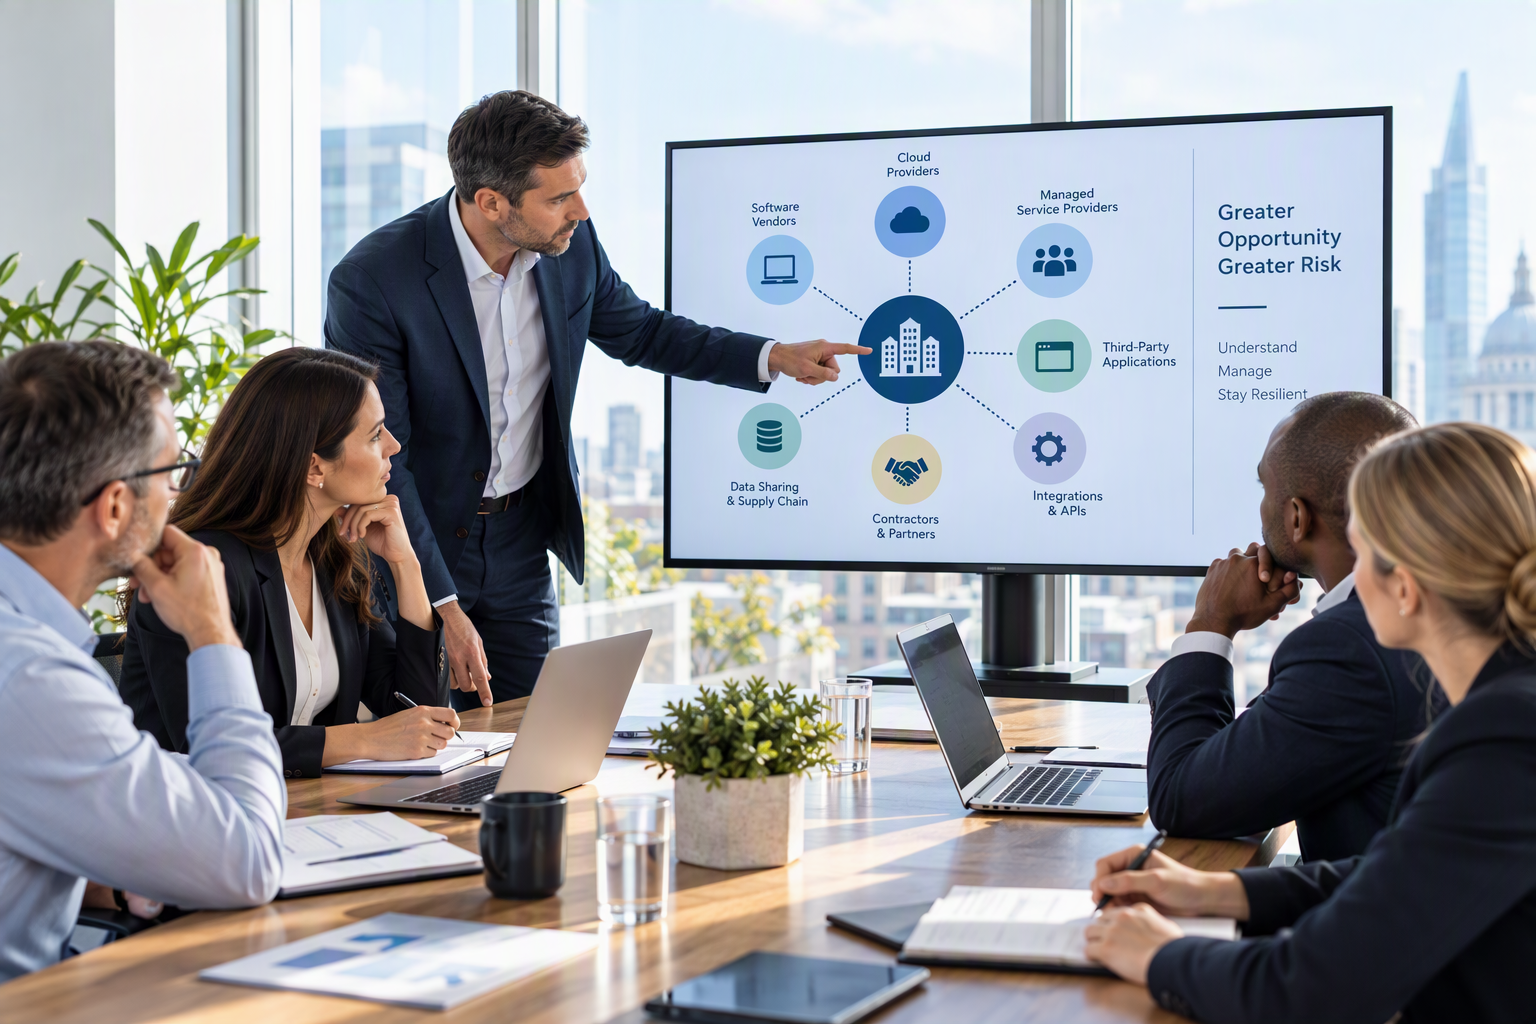
Consider a growing financial technology company… Three years ago, the organisation had a single customer portal, a small internal team and a relatively straightforward infrastructure. Today it might operate multiple customer-facing applications, third-party payment processors, cloud environments, development pipelines and dozens of API integrations.
Every individual change was reviewed and approved. Yet nobody stepped back to assess how these changes interact collectively. An attacker does not see separate systems. An attacker sees pathways.
A low-risk vulnerability in one application may provide access to another system. Excessive permissions granted for convenience may expose sensitive data. An overlooked service account may become the starting point for a larger compromise. These attack paths often emerge only after years of operational growth.
The Warning Signs Most Organisations Miss
Security drift rarely generates alerts. There is no dashboard that suddenly displays a message saying, “Your organisation has gradually become vulnerable.” Instead, the warning signs appear in everyday operations.
Teams begin to lose visibility over who has access to what. Documentation no longer reflects reality. Legacy systems become difficult to identify. User accounts accumulate, integrations multiply and exceptions become permanent. Over time, complexity replaces clarity.
This is often the point at which organisations mistakenly believe they need more security tools. In reality, they may first need a clear understanding of their current environment.
Why Traditional Audits Often Miss the Problem
Compliance assessments, policies and vulnerability scans remain important. However, security drift frequently develops in the spaces between these controls. An automated scanner can identify known vulnerabilities. It cannot always understand how an attacker might exploit several seemingly harmless weaknesses together.
A policy may require least-privilege access. It does not confirm that years of business change have actually maintained that principle. This is where organisations often discover the value of penetration testing.
A skilled tester examines the environment as an attacker would. Rather than reviewing systems individually, they explore how systems interact, how permissions overlap and how small weaknesses can combine into genuine business risk.
The Cost of Waiting
Many organisations only investigate security when a compliance deadline approaches. Unfortunately, attackers do not operate according to audit schedules. The longer security drift continues unchecked, the greater the likelihood that hidden exposures accumulate inside the environment. The good news is that security drift is entirely manageable.
Organisations that periodically review their environments, validate assumptions and perform independent security testing are far more likely to identify weaknesses before somebody else does. Cybersecurity is not simply about defending what existed yesterday, it is about understanding what exists today. Because the greatest risk is rarely the vulnerability you already know about. It is the vulnerability that appeared gradually while the business was busy growing.