The Security Weaknesses Hiding in Plain Sight
When organisations think about cybersecurity vulnerabilities, they usually picture outdated software, weak passwords, exposed services, or misconfigured cloud environments. These are genuine risks, and they frequently appear during penetration tests. However, one of the most common vulnerabilities we encounter is something entirely different. It is familiarity cyber risk.
Over time, people become comfortable with the systems they use every day. Processes become routine. Workarounds become accepted. Administrative permissions remain in place because removing them feels inconvenient. Shared accounts continue to exist because “they have always been there.” The longer these conditions remain unchanged, the less noticeable they become.
Ironically, the people closest to a system are often the least likely to spot its weaknesses.
The Office Door Nobody Notices
Imagine walking into an office every day through the same entrance. On the first day, you might notice that the door does not close properly. Two weeks later, you stop thinking about it. Six months later, you no longer see it at all. The fault has not disappeared. It has simply become normal. Cybersecurity works exactly the same way.
We regularly encounter environments where internal teams are highly competent and security-conscious, yet certain risks have become part of everyday operations. Nobody questions them anymore because they have become familiar.
During a recent penetration testing engagement, a client was surprised when we identified excessive user permissions that provided access far beyond what employees required. The permissions had existed for years without issue. They had survived system migrations, staff changes, audits and security reviews.
The risk was not difficult to find. It was simply no longer visible to those working with the environment every day.
Why Attackers See Things Differently
Attackers have one significant advantage. They do not know which systems are considered critical but they arrive with fresh eyes. They also do not know which processes are accepted exceptions or which permissions were granted for historical reasons. Attackers simply look for opportunities.
An attacker sees an exposed API endpoint, an old administrator account that nobody remembers and an attacker identifies a test environment connected to production. What appears normal to an internal team may appear highly unusual to someone assessing the environment objectively. This difference in perspective explains why organisations often discover security weaknesses shortly after engaging an independent penetration testing provider.
The finding itself may not be sophisticated. The value often comes from seeing the environment differently.
The Hidden Cost of “We’ve Always Done It This Way”
Every organisation develops operational shortcuts. This is natural. Business priorities evolve faster than systems can keep up. People find efficient ways to get work done. Temporary solutions become permanent solutions. The challenge arises when convenience quietly overrides security.
Consider some examples:
- A service account is given broad privileges to solve an urgent issue and those privileges are never revisited.
- A legacy application remains accessible because removing it feels risky.
- Multi-factor authentication is not enforced on a small administrative platform because nobody has experienced a problem.
- Third-party suppliers retain access long after projects have finished.
None of these situations necessarily indicate poor security management. They simply reflect how organisations operate in the real world. Unfortunately, attackers operate in the real world too.
Why Penetration Testing Is So Effective
Many people assume penetration testing is primarily about technical exploitation. That is certainly part of the process. However, one of the greatest values of penetration testing is independent perspective.
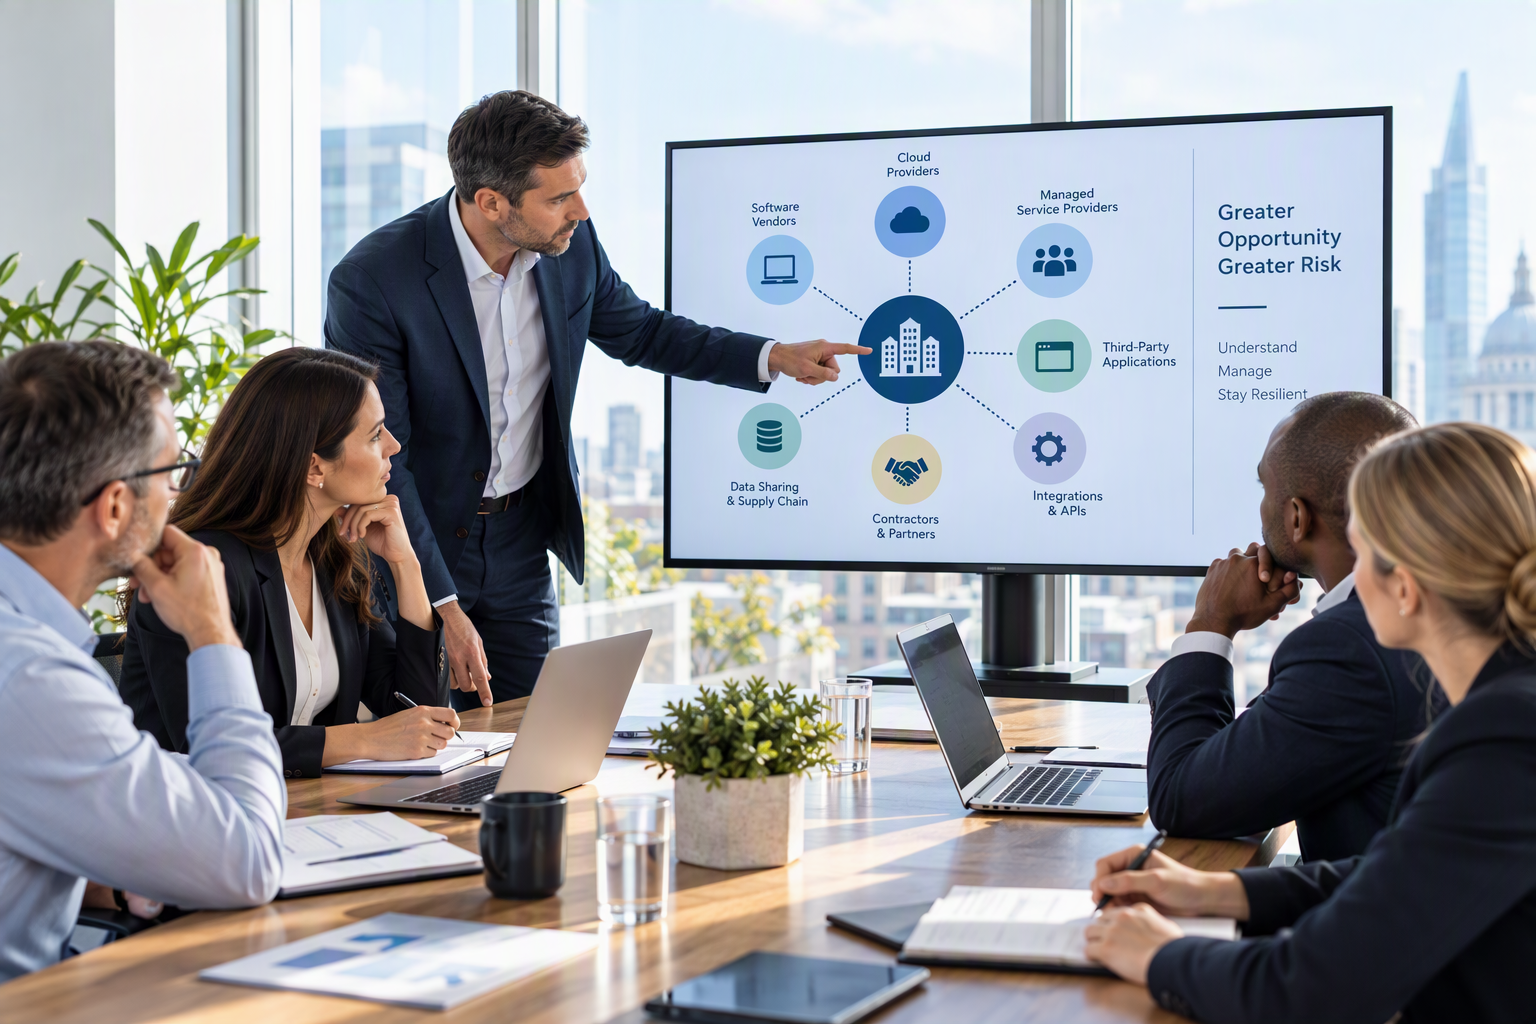
A good penetration tester approaches an environment without assumptions. Every permission, trust relationship, integration, access path and configuration is questioned. The objective is not just to identify vulnerabilities. It is to discover risks that have become invisible through familiarity.
This is why organisations are often surprised by penetration test findings. Not because the vulnerabilities are extremely complex, but because nobody had thought about them from a different perspective.
Security Drift Begins With Familiarity
This concept also connects closely to security drift. Systems change continuously. New employees join. New applications are deployed. Cloud environments expand. APIs are added. Business priorities shift. Small changes accumulate over time. Each individual change appears harmless however, collectively, they can create significant exposure.
Without independent assessment, organisations may not recognise how far their security posture has drifted from the original design. Familiarity makes that drift difficult to see.
The Most Dangerous Vulnerabilities Are Often the Most Obvious
The cybersecurity industry frequently celebrates sophisticated attacks and advanced threats. In reality, many successful breaches begin with something far simpler. An unnecessary permission, an overlooked integration an old account, a forgotten exception, a familiar risk that nobody questioned… That is why independent penetration testing remains one of the most valuable cybersecurity investments an organisation can make.
The goal is not merely to identify technical vulnerabilities. The goal is to challenge assumptions, uncover hidden exposure, and see the environment through the eyes of someone who has never seen it before.
Because sometimes the most dangerous vulnerability is not the one nobody knows about. It is the one everybody has stopped noticing.