The creeping risk
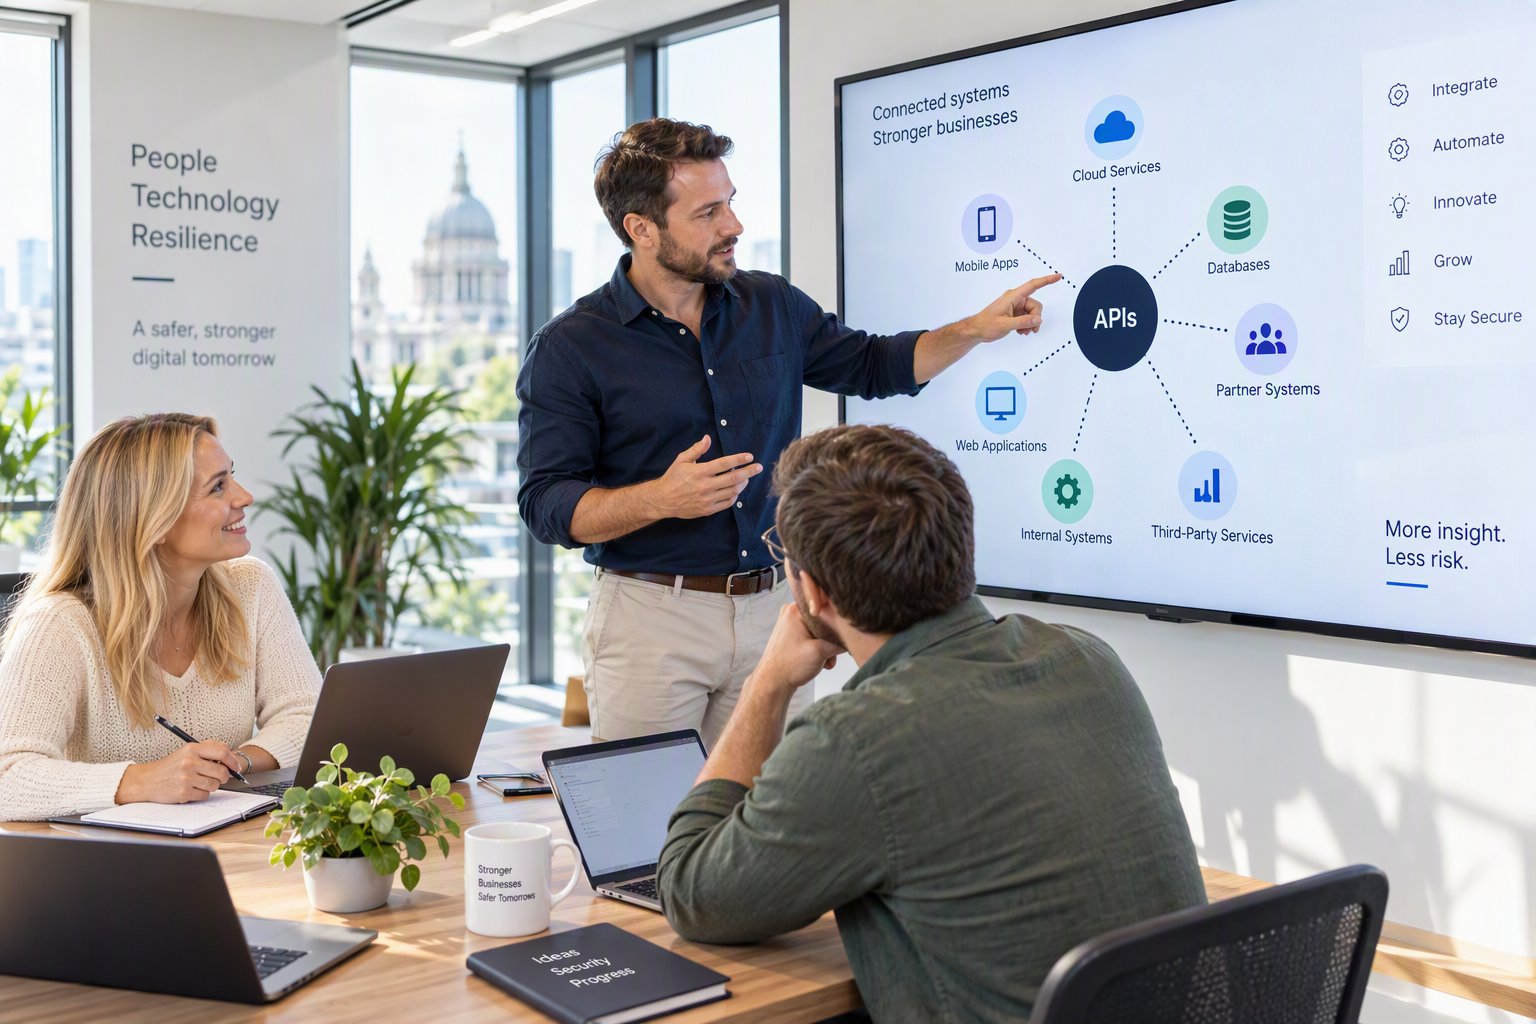
When business leaders think about cybersecurity, they often think about websites, laptops, cloud platforms and email systems. Few think about APIs. Yet APIs are quietly powering a significant proportion of modern business operations. Every time data moves between a CRM and an ERP platform, an online portal checks account information, a mobile application retrieves customer records, or a cloud service synchronises data with another system, there is a good chance an API is involved. For many organisations, APIs have become the digital glue that holds business processes together. The problem is that many organisations have far more APIs than they realise and consequently more API security risks.
Over the past decade, businesses have adopted cloud applications at an extraordinary rate. New integrations are added, new software platforms are introduced, and data is exchanged across an increasing number of systems. Each integration creates efficiency and automation, but it can also create additional attack surfaces. In many cases, security attention remains focused on the systems that employees can see. The APIs operating behind the scenes receive far less scrutiny. This can be a costly mistake.
What makes APIs so attractive from all sides?
Unlike traditional websites, APIs are designed specifically to exchange data and perform actions. They often provide direct access to customer records, financial information, operational workflows and business logic. As a result, attackers frequently view them as highly attractive targets.
We regularly encounter organisations that have invested heavily in securing their networks and applications while giving comparatively little attention to the APIs connecting those systems together. The assumption is often that because an API is not visible to the public, it is less likely to be targeted. Unfortunately, attackers do not share that assumption. Many API vulnerabilities are not particularly technical in nature. They arise from simple design oversights.
An attacker may discover they can access data belonging to another customer simply by changing a number within a request. A poorly configured API may expose information without proper authentication. Excessive permissions may allow users to perform actions they were never intended to perform. The application itself may appear secure while the underlying API quietly exposes sensitive information.
What makes API risk especially challenging is that business growth often increases exposure.
Risk multiplies as the organisation grows
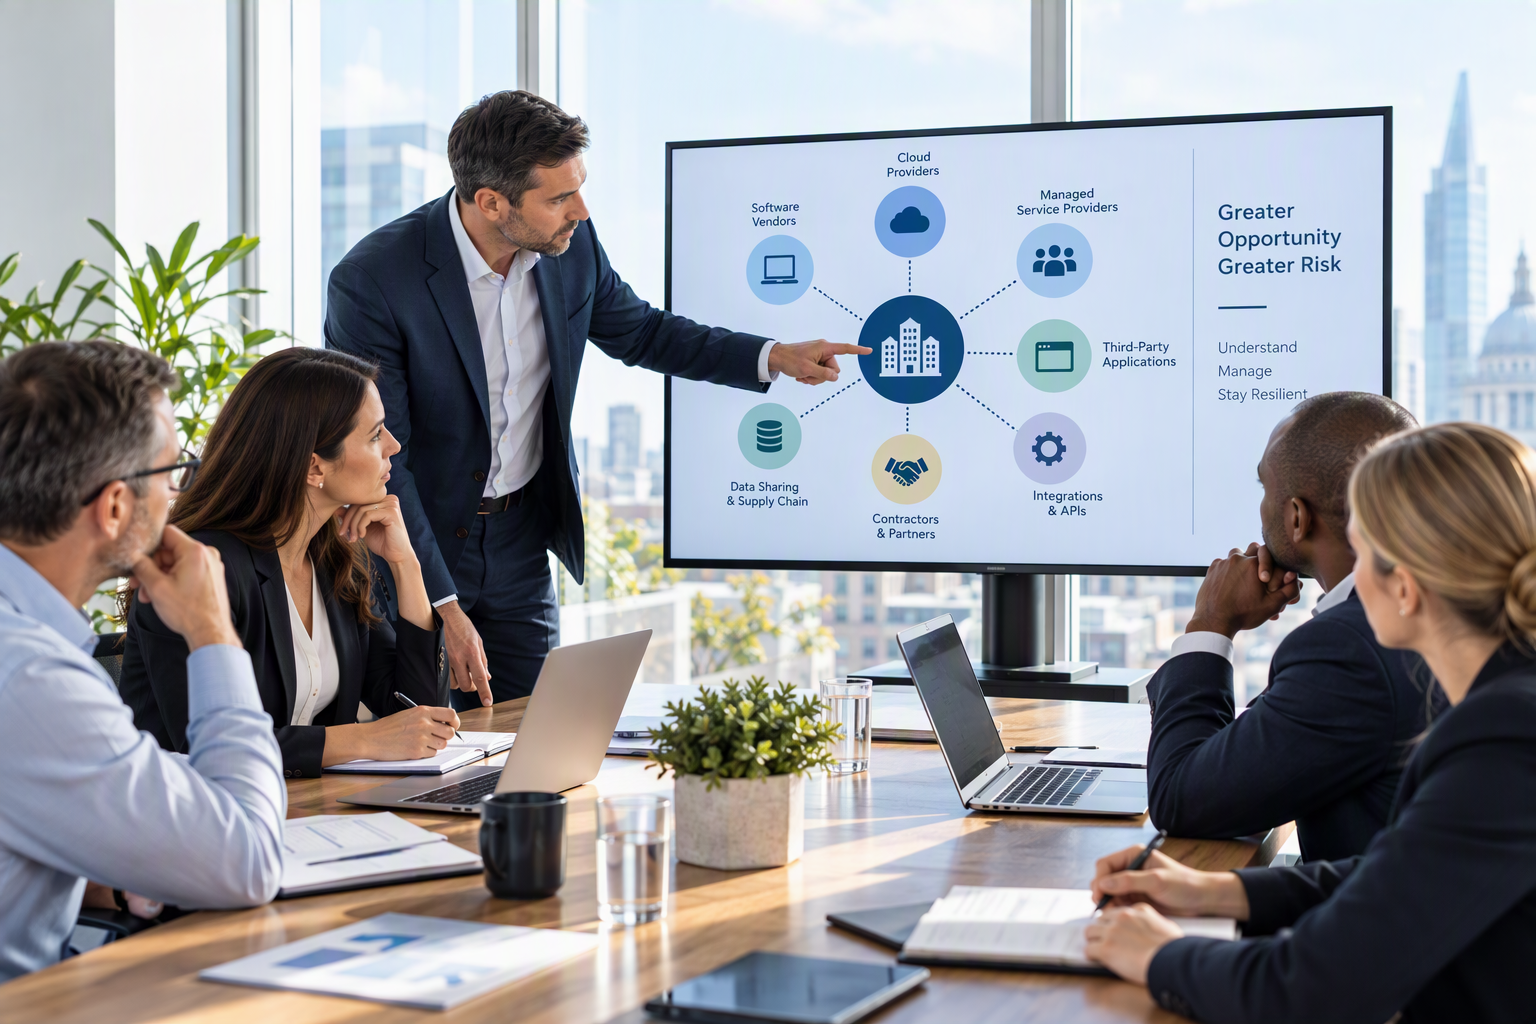
Each new partner integration, mobile application, customer portal and SaaS implementation can introduce additional APIs. Over time, organisations create a complex ecosystem of interconnected services where a weakness in one component can affect many others. As these environments grow, visibility often decreases.
Security teams know what systems they own, but they may not fully understand all the ways those systems communicate with one another. That is where penetration testing becomes particularly valuable.
An effective API penetration test examines how APIs authenticate users, validate requests, control access to data and protect critical business functions. It helps organisations identify vulnerabilities before attackers do and provides a clearer understanding of the risks that exist within their integration landscape.
Importantly, API penetration testing also reveals risks that automated scanners frequently miss. Many API vulnerabilities involve business logic rather than software flaws. Understanding how an attacker might abuse functionality often requires human analysis and real-world testing.
The organisations that manage API security most effectively are not necessarily those with the fewest integrations. They are the organisations that understand their API landscape, test it regularly and ensure security evolves alongside the business. After all, APIs are now critical business infrastructure. If attackers increasingly target them, they deserve the same level of attention as every other critical system. And for many organisations, the first step is simply discovering how many APIs they actually have.