Your Next Cyber Incident Might Start During Your Best Year Ever
When business leaders think about cybersecurity risk, they often associate it with disruption, economic uncertainty, budget cuts or operational challenges. However, some of the most significant cybersecurity weaknesses emerge during periods of success. In fact, many organisations become more vulnerable when everything appears to be going well. Growth creates opportunity however it also creates complexity, and complexity is where cybersecurity problems often begin. Business growth cybersecurity risk is a challenge that one needs to be aware of.
Success Changes Everything
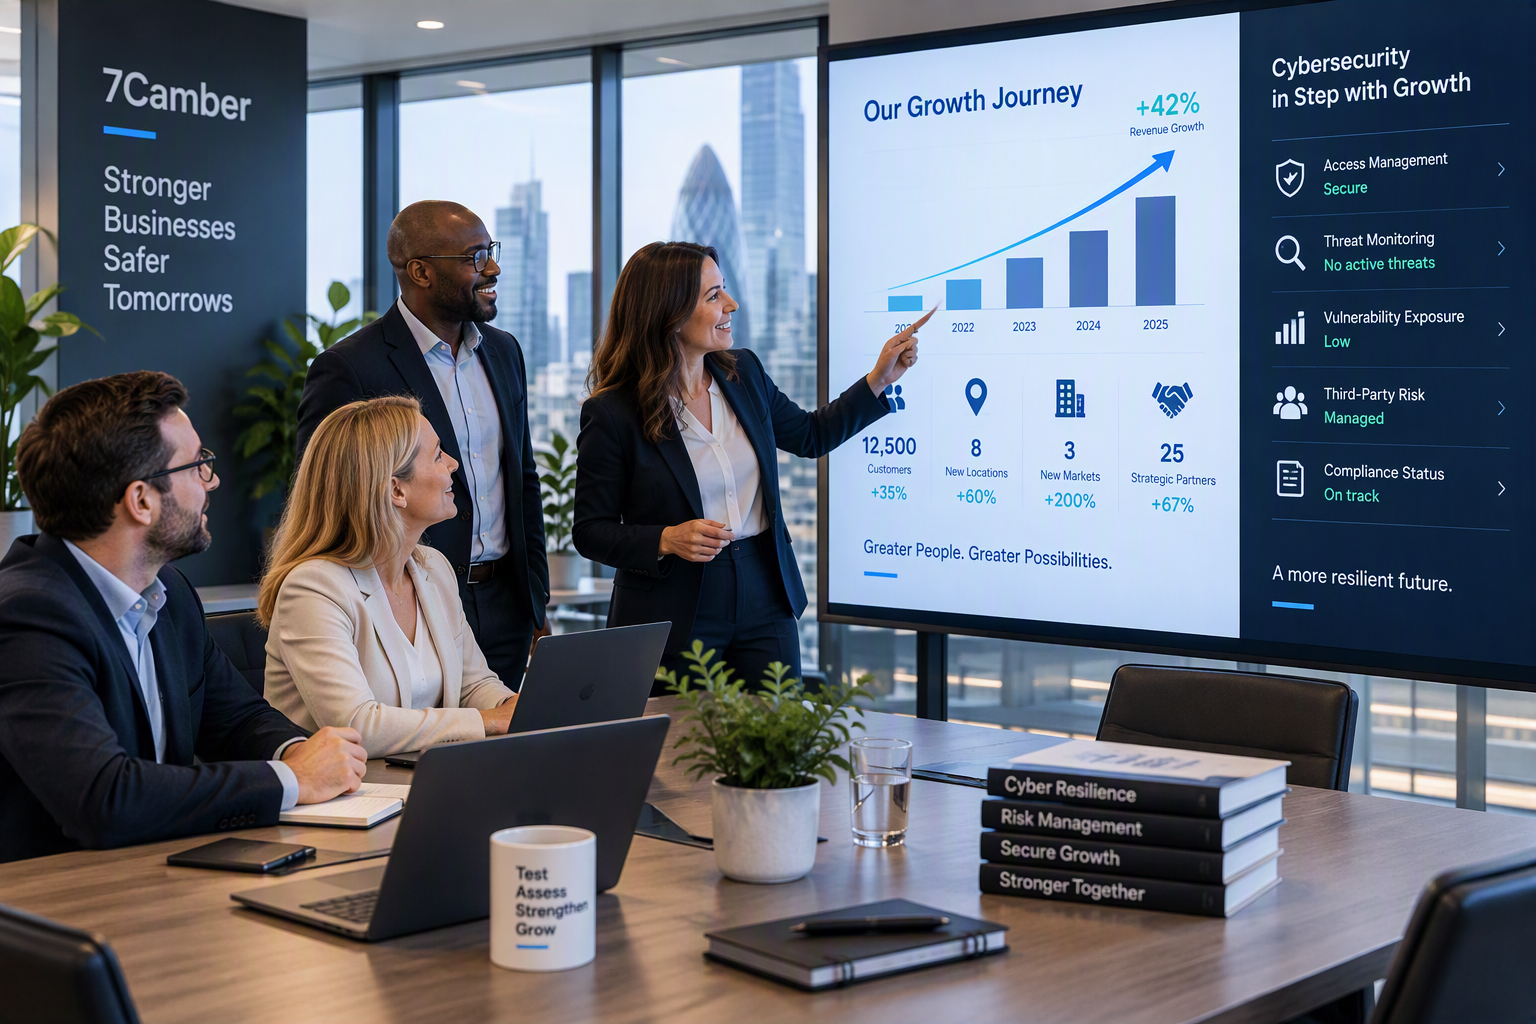
Picture an organisation that has experienced a strong year. Revenue is growing, new customers are joining, more staff are being recruited, new systems are being implemented and additional suppliers are being onboarded. Business leaders are focused on maintaining momentum and that is exactly as it should be. The challenge is that cybersecurity rarely expands at the same pace. While the business accelerates, risk quietly accumulates in the background.
Growth Creates New Attack Surfaces
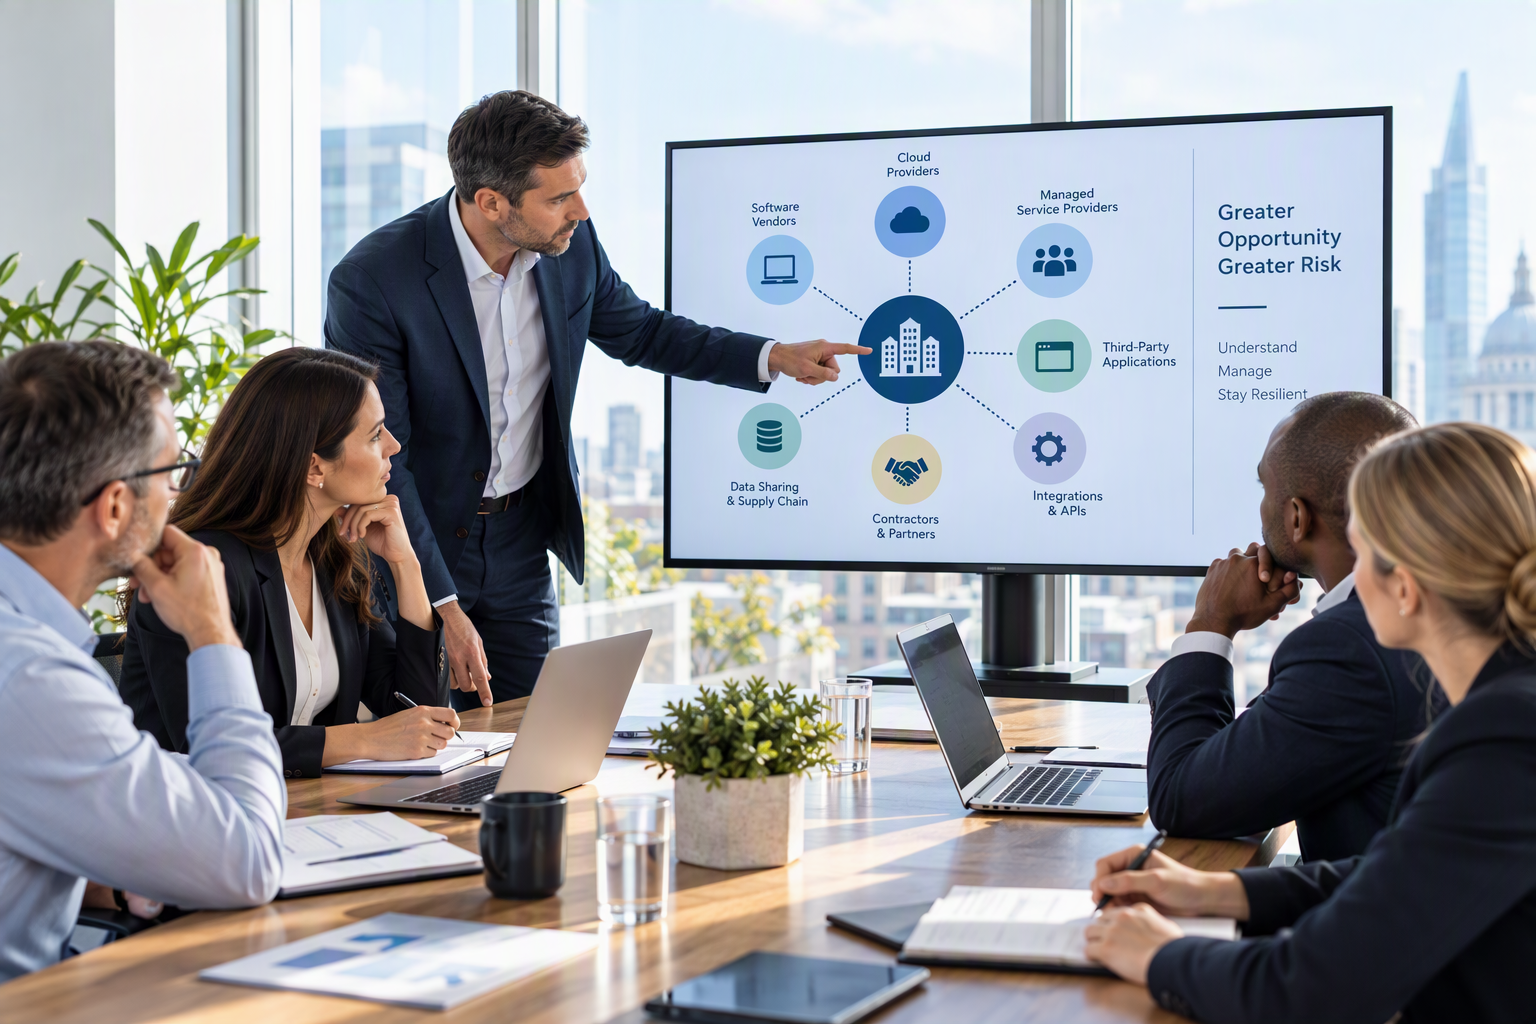
Every new employee requires access, new suppliers introduce trust relationships, every new software platform expands the technology footprint and every acquisition, integration or expansion project adds further complexity. Each change may seem insignificant on its own however, collectively, they can transform a manageable environment into one that is difficult to govern effectively. This is how business growth cybersecurity risk becomes a tangible reality.
We frequently see this during cybersecurity reviews: The organisation has not made a poor decision; it has simply made many good business decisions in a short period of time. The unintended consequence is increased exposure.
The Hidden Cost of “We’ll Fix That Later”
Rapid growth often requires speed and teams focus on delivering outcomes, processes are streamlined and workarounds are accepted. As a consequence, future improvements are postponed. The reasoning is understandable since the immediate priority is supporting business growth. The problem is that temporary solutions have a habit of becoming permanent and what started as a short-term exception can eventually become an everyday operating practice. Over time, security debt accumulates in much the same way technical debt accumulates in software development. Eventually, somebody has to pay it back.
Why Attackers Pay Attention to Growing Organisations
Cyber criminals are not only interested in large enterprises, they are interested in organisations that are changing. Periods of rapid change often create:
- Inconsistent processes
- Incomplete documentation
- Excessive user permissions
- New technology deployments
- Increased third-party access
- Reduced visibility of assets and data
Attackers understand that people are focused on business priorities and that security controls can sometimes receive less attention during these periods. That is precisely what makes growing organisations attractive targets.
What We Commonly Observe
When conducting assessments and penetration tests, we often find that risks emerge from expansion rather than neglect. Examples include:
- Former employees retaining access after organisational growth
- Cloud platforms deployed without sufficient governance
- New business applications operating outside established security processes
- Suppliers gaining broad access that is never reviewed
- Sensitive data spreading across multiple systems during expansion projects
None of these situations usually result from poor intentions or inadequate leadership, more often, they are a by-product of success since the business has moved faster than its control environment.
Growth and Cybersecurity Must Scale Together
The solution is not to slow growth, it is to ensure that resilience scales alongside it. Organisations should periodically ask:
- Do we know who has access to what?
- Have our suppliers introduced new risks?
- Are our security controls still appropriate for our current size?
- Has our attack surface changed over the last 12 months?
- Would we detect suspicious activity in newly deployed systems?
- Have we independently tested our security posture recently?
These questions become increasingly important as organisations mature.
In summary…
Many organisations prepare for tough times yet fewer prepare for successful times. Yet growth changes people, processes and technology at a remarkable pace. The cybersecurity controls that worked perfectly twelve months ago may no longer be sufficient for the organisation you have become today. Success is something every business strives for and the challenge is ensuring that cybersecurity grows with it because sometimes the conditions that create your biggest opportunities also create your next cyber incident.