No security incidents no penetration test.
One of the most common reasons organisations postpone a penetration test is surprisingly simple:
“We’ve never had a security incident.”
No security incidents… no penetration test. At first glance, that sounds reasonable. If nothing bad has happened, why spend time and money looking for security weaknesses? The problem is that cybersecurity does not work that way. The absence of a known security incident does not automatically mean your organisation is secure. In fact, many businesses only discover weaknesses after an attacker has already found them.
The reality is uncomfortable but important: not knowing about a problem is very different from not having one.
Security Incidents Are Not Always Visible
Most people imagine cyber attacks as dramatic events. Systems stop working, data appears online, news headlines follow. However, many compromises are far quieter. Attackers often spend weeks or even months inside networks without raising suspicion. Their objective is to remain unnoticed while they gather information, identify opportunities, or prepare for future attacks.
As a result, organisations can believe they are secure simply because no obvious incident has occurred. A penetration test helps answer a different question: If an attacker targeted us today, what could they find and exploit?
Cyber Criminals Only Need One Weakness
Organisations often invest in firewalls, antivirus software, endpoint protection, and employee awareness training. These are all important controls, however attackers are not looking for perfection. They are looking for a single weakness.
That weakness could be:
- An overlooked internet-facing service
- A vulnerable web application
- Weak internal permissions
- An insecure API
- An exposed administrative interface
- A misconfigured cloud service
Any one of these issues could provide an attacker with a foothold. Penetration testing helps identify these weaknesses before someone with malicious intent discovers them.
Business Changes Create New Risks
Even organisations with strong security practices experience constant change. Consider what may have changed in the last year:
- New software deployments
- Cloud migrations
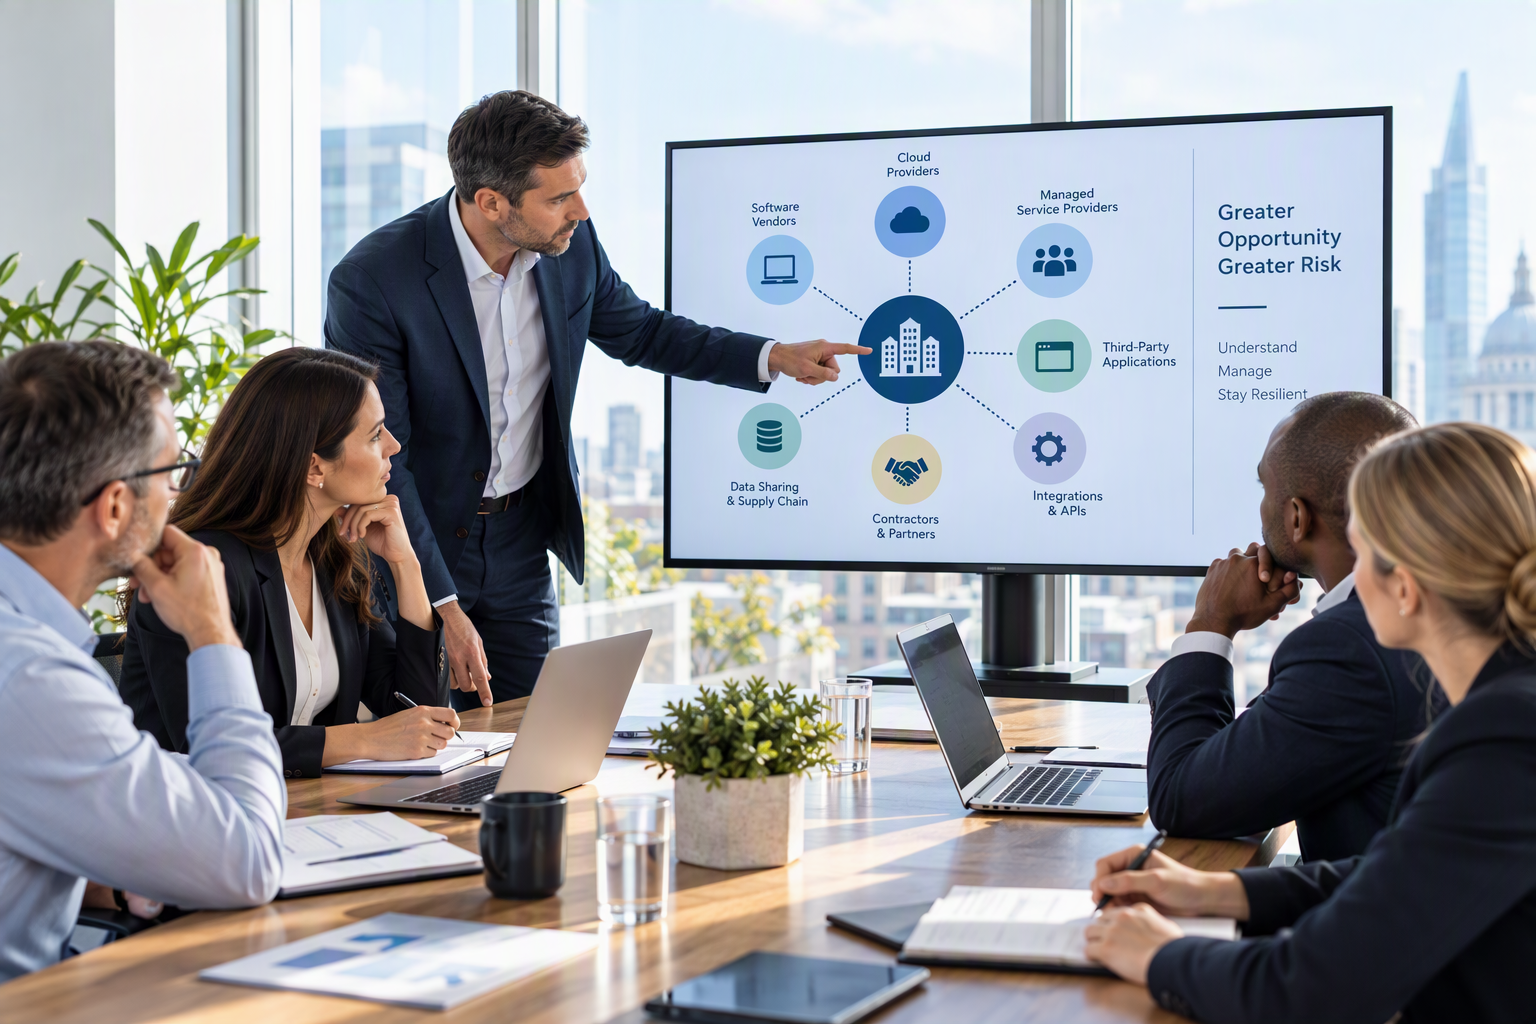
- Third-party integrations
- Remote working arrangements
- Infrastructure upgrades
- New employees and contractors
Every change introduces the possibility of new vulnerabilities. Security is not a one-off achievement, it is an ongoing process. This is why organisations that have never experienced an incident still carry out periodic penetration testing.
Compliance Is Not the Same as Security
Some businesses only consider security assessments when regulations require them. While compliance is important, it should not be the sole reason for testing. A penetration test provides value beyond satisfying auditors. It helps organisations:
- Understand real-world attack paths
- Prioritise remediation efforts
- Validate existing security controls
- Reduce business risk
- Demonstrate due diligence to stakeholders
Most importantly, it provides evidence that your security measures are working as intended.
The Cost of Waiting
After a breach, organisations often ask: “How was this not discovered earlier?”
The answer is frequently simple: “Nobody looked for it.“
Security weaknesses rarely fix themselves. Over time, they often become easier for attackers to discover and exploit. The costs associated with a breach can include:
- Operational disruption
- Incident response expenses
- Regulatory scrutiny
- Customer notification requirements
- Reputational damage
- Loss of business confidence
Compared with the potential impact of a successful attack, proactive testing is usually a modest investment.
Penetration Testing Provides Clarity
One of the greatest benefits of penetration testing is certainty. Instead of making assumptions about security, organisations receive an independent assessment of their actual exposure. The results help answer important questions:
- How difficult would it be for an attacker to gain access?
- Which vulnerabilities present the highest risk?
- Are our security controls working correctly?
- Where should we prioritise improvements?
These answers allow organisations to make informed decisions based on evidence rather than assumptions.
The Real Question
When organisations say, “We’ve never had a security incident,” they are often asking the wrong question.
The question should not be: “Have we been compromised?“
The better question is: “How confident are we that an attacker could not compromise us today?“
Penetration testing helps provide that confidence. Because in cybersecurity, the organisations that test for weaknesses before attackers find them are usually the ones that avoid becoming tomorrow’s cautionary tale.
Take away summary…
Never experiencing a known security incident is good news. However, it should not be treated as proof that your organisation is secure. Threats evolve, systems change, and vulnerabilities emerge continuously. A penetration test provides an objective view of your security posture, helping you discover weaknesses before criminals do.
The best time to identify a security problem is before it becomes a security incident.
If your organisation has never undergone a penetration test, or if it has been some time since the last assessment, now may be the right moment to find out what attackers could see.