Cybersecurity After a Merger: The Hidden Risks Companies Often Miss
For most organisations, a merger or acquisition is an exciting milestone. The deal is signed, teams are introduced, systems begin to merge and leaders focus on growth opportunities, operational efficiencies, and delivering value to customers.
Yet there is one important question that often receives far less attention than it deserves: What happens to cybersecurity when two organisations become one?
Many business leaders assume that if both companies were operating successfully before the merger, they must also be secure after the merger. Unfortunately, that assumption can be dangerous.
A merger often creates one of the largest cybersecurity changes an organisation will ever experience. Networks are connected. New users gain access. Applications are integrated. Sensitive data begins to flow between environments. Each of these changes can introduce new vulnerabilities and the result is simple:
Even if both organisations were reasonably secure before the merger, the combined organisation may be significantly more exposed afterwards.
Why Mergers Create New Cyber Risks
Imagine buying a new house…
From the outside, everything looks perfect but once you move in, you discover faulty wiring, broken locks, and a leaking roof. The same principle applies to technology. During a merger, organisations inherit systems, processes, suppliers, and security practices that may not be fully understood. Questions soon emerge:
- Are all systems properly patched?
- Are old user accounts still active?
- Are there forgotten servers?
- Are access rights appropriate?
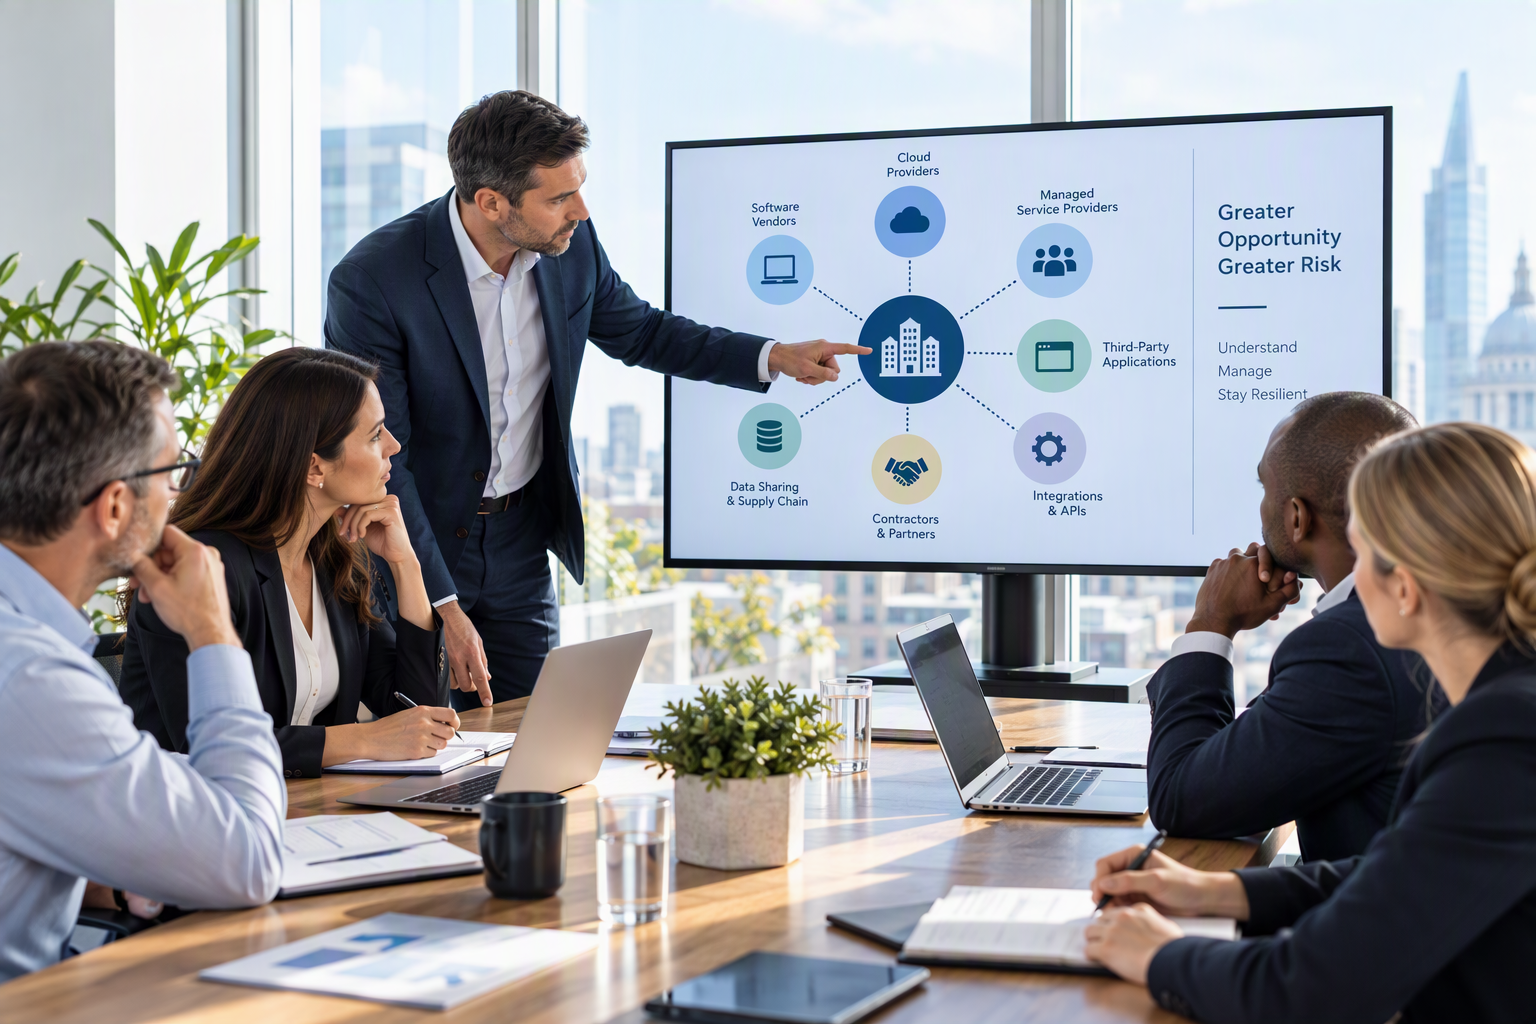
- Are third-party suppliers secure?
- Are APIs and integrations introducing new weaknesses?
In many cases, nobody knows the complete answer.
The Problem with Trusting Previous Assessments
A common misconception is that security assessments carried out before the merger remain valid afterwards. They do not. A penetration test reflects a specific environment at a specific point in time. Once systems are connected, that environment changes, for example: A low-risk vulnerability in Company A may become a high-risk vulnerability when it can suddenly communicate with systems from Company B.
Similarly, a legacy application that previously contained limited information may gain access to sensitive customer data after integration. The context changes and the risk changes.
The New Attack Paths Nobody Expected
Cyber attackers look for opportunities and mergers often create exactly that. When networks are connected quickly, new routes between systems become available. What was once isolated may now be accessible. Attackers do not care which company originally owned the vulnerable system. They only care whether it provides a path to valuable information. This means that a single overlooked weakness can sometimes give an attacker access to:
- Customer data
- Employee information
- Financial systems
- Intellectual property
- Cloud environments
- Administrative accounts
A problem that appeared small before integration can become much larger afterwards.
Why Penetration Testing Matters After a Merger
This is where penetration testing becomes extremely valuable. A properly conducted penetration test helps organisations understand how their newly integrated environment behaves from an attacker’s perspective. Rather than reviewing systems individually, testers examine how the combined environment works as a whole. They assess:
- Network connectivity
- Access controls
- Authentication mechanisms
- Web applications
- APIs
- Cloud configurations
- Privilege escalation opportunities
- Lateral movement paths
The objective is simple: Find weaknesses before attackers do.
More importantly, organisations gain practical insight into which risks matter most.
A Business Decision, Not Just a Technical One
Some leaders view penetration testing as an IT exercise while in reality, it is a business risk exercise. The consequences of a cyber incident after a merger can be significant and they may include:
- Regulatory scrutiny
- Operational disruption
- Customer distrust
- Financial losses
- Reputational damage
- Delays in integration programmes
Identifying security weaknesses early can help avoid these outcomes and support a smoother transition.
The Best Time to Assess Security
Many organisations wait until their integration programme is complete before reviewing cybersecurity however by then, weaknesses may already exist. A better approach is to include security testing as part of the integration journey. Ideally, assessments should be carried out:
- Before systems are connected
- During major integration phases
- After significant technology changes
- When new services become accessible
- Before handling sensitive shared data
This provides continuous visibility during a period of rapid change.
So are mergers all bad from a cybersecurity perspective?
Successful mergers are built on confidence: Confidence in people, in processess and confidence in technology. Yet cybersecurity is often one of the least visible risks in a merger project. The reality is that bringing two organisations together usually creates new attack surfaces, new complexities, and new opportunities for cyber criminals. The good news is that these risks can be identified and managed.
A penetration test carried out after a merger provides an independent view of the combined environment and helps organisations understand where hidden weaknesses may exist.
When two companies merge, cyber risk does not automatically stay the same, sometimes, without anyone noticing, it doubles…and that is a risk worth understanding.