Your Next Supplier Could Be Your Next Security Incident
When organisations think about cybersecurity, they usually look inward. They focus on their firewalls, their employees, their devices and their systems. They invest in security tools, strengthen policies and improve monitoring. All these measures are important. Yet many businesses continue to overlook one of the fastest-growing sources of cyber risk: Their suppliers, i.e. third-party cybersecurity risk.
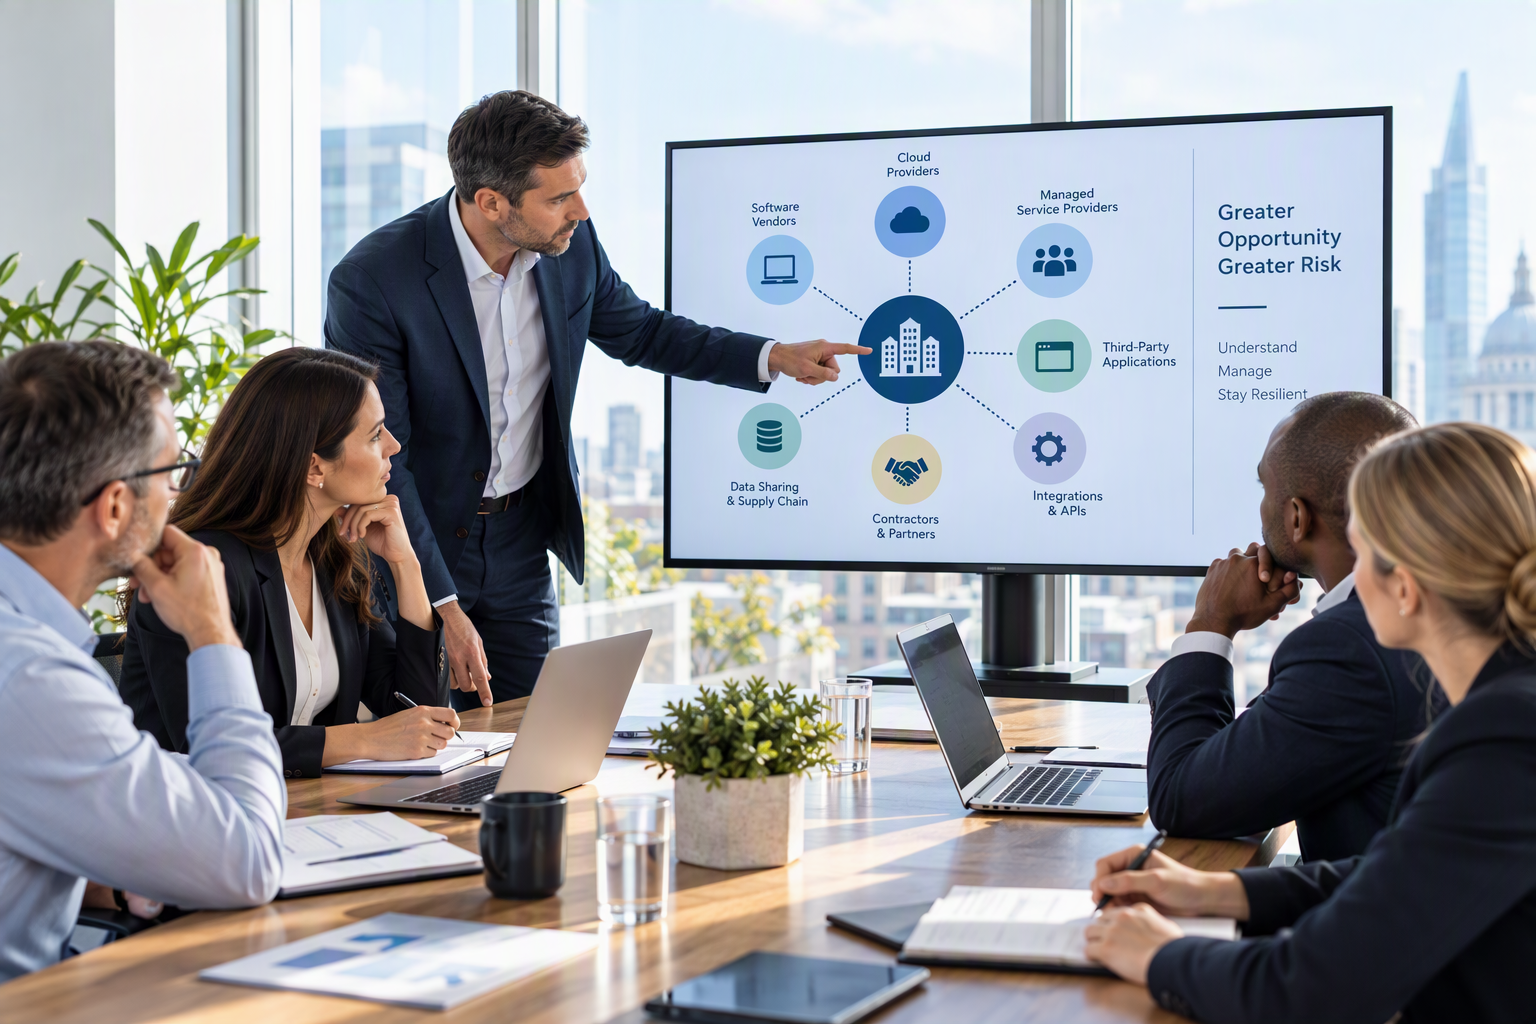
Every time a new supplier is onboarded, a level of trust is created. Access may be granted to systems, networks, applications, data or business processes. Files may be exchanged automatically through integrations, external consultants may receive accounts, cloud providers may host sensitive information and software vendors may connect directly into critical environments. Essentially, the supplier relationship becomes part of the organisation’s operating model and that is where the risk begins.
Many organisations conduct thorough commercial due diligence before selecting a supplier. They compare prices, review service levels and evaluate capabilities. Cybersecurity, however, is often treated as a secondary consideration. This creates a dangerous imbalance.
A supplier does not need to suffer a major breach for problems to arise. An inadequately secured remote access mechanism, weak authentication controls or a poorly protected application can create an attack path directly into your organisation. In many cases, attackers actively target smaller suppliers because they are easier to compromise than the larger organisations they serve.
The reality is simple. An organisation’s security posture is only as strong as the weakest trusted connection within its ecosystem.
A Trusted Supplier As My Next Security Risk?
At 7Camber, we regularly see organisations invest heavily in protecting their own infrastructure while overlooking the security controls their third parties use. The issue becomes even more significant as businesses adopt more cloud services, outsource specialist functions and integrate with an increasing number of external partners.
What makes third-party cybersecurity risk particularly challenging is that it often develops gradually. Individual supplier connections may appear low risk when viewed in isolation. Over time, however, dozens or even hundreds of trusted relationships accumulate. Each one introduces new access paths, new dependencies and new opportunities for attackers. Business growth can unintentionally expand the attack surface.
This does not mean organisations should avoid digital transformation or supplier partnerships. Quite the opposite. External providers deliver expertise, innovation and efficiency that often drive business success. The objective is not to eliminate supplier relationships but to understand and manage the risks they create. That starts with asking better questions.
How does the supplier protect sensitive information? What security controls are in place? Has the supplier undergone independent security testing? How quickly would they detect and respond to a cyber incident? What access do they really need?
These conversations should happen before contracts are signed, not after an incident occurs. Organisations should also periodically review existing supplier relationships. Security is not static. Businesses change, technologies evolve and threat actors continuously adapt their tactics. A supplier assessed two years ago may present a very different risk profile today.
The most resilient organisations recognise that cybersecurity extends beyond their own walls. They view security as part of an interconnected ecosystem where every trusted relationship matters.
In today’s connected business environment, your next security incident may not begin with your employees, your systems or your network. Your newest supplier could trigger the incident, and you may not realise it until long after your team has forgotten the onboarding process.