
-
We Merged Two Companies Successfully. So Why Did Our Cyber Risk Double?
When two companies merge, IT systems, users, applications, and data are combined at speed. While commercial integration often receives most…
-
We’ve Never Had a Security Incident, So Why Would We Need a Penetration Test?
Many organisations believe they are secure simply because they have never suffered a known cyber incident. In reality, the absence…
-
We Have Cyber Insurance, So We’re Covered… Right?
Cyber insurance can help organisations recover financially after a cyber incident, but it cannot prevent attacks from happening. Discover why…
-
The Hidden Cost of Waiting: The Best Time to Run a Penetration Test Is Before the Hacker Does
Many organisations only think about penetration testing after a cyber incident. By then, the damage may already be done. Learn…
-
The Hidden Message in the EU Cybersecurity Audit: Why Penetration Testing Matters More Than Ever
A recent European Court of Auditors report highlights growing cybersecurity challenges across Europe, including detection gaps, incident under-reporting and increasing…
-
Privilege Escalation Vulnerabilities: The Hidden Risk That Can Turn a Minor Breach into a Major Incident
Many organisations focus on preventing cyber attacks but overlook the weaknesses that allow attackers to gain greater access after a…
-
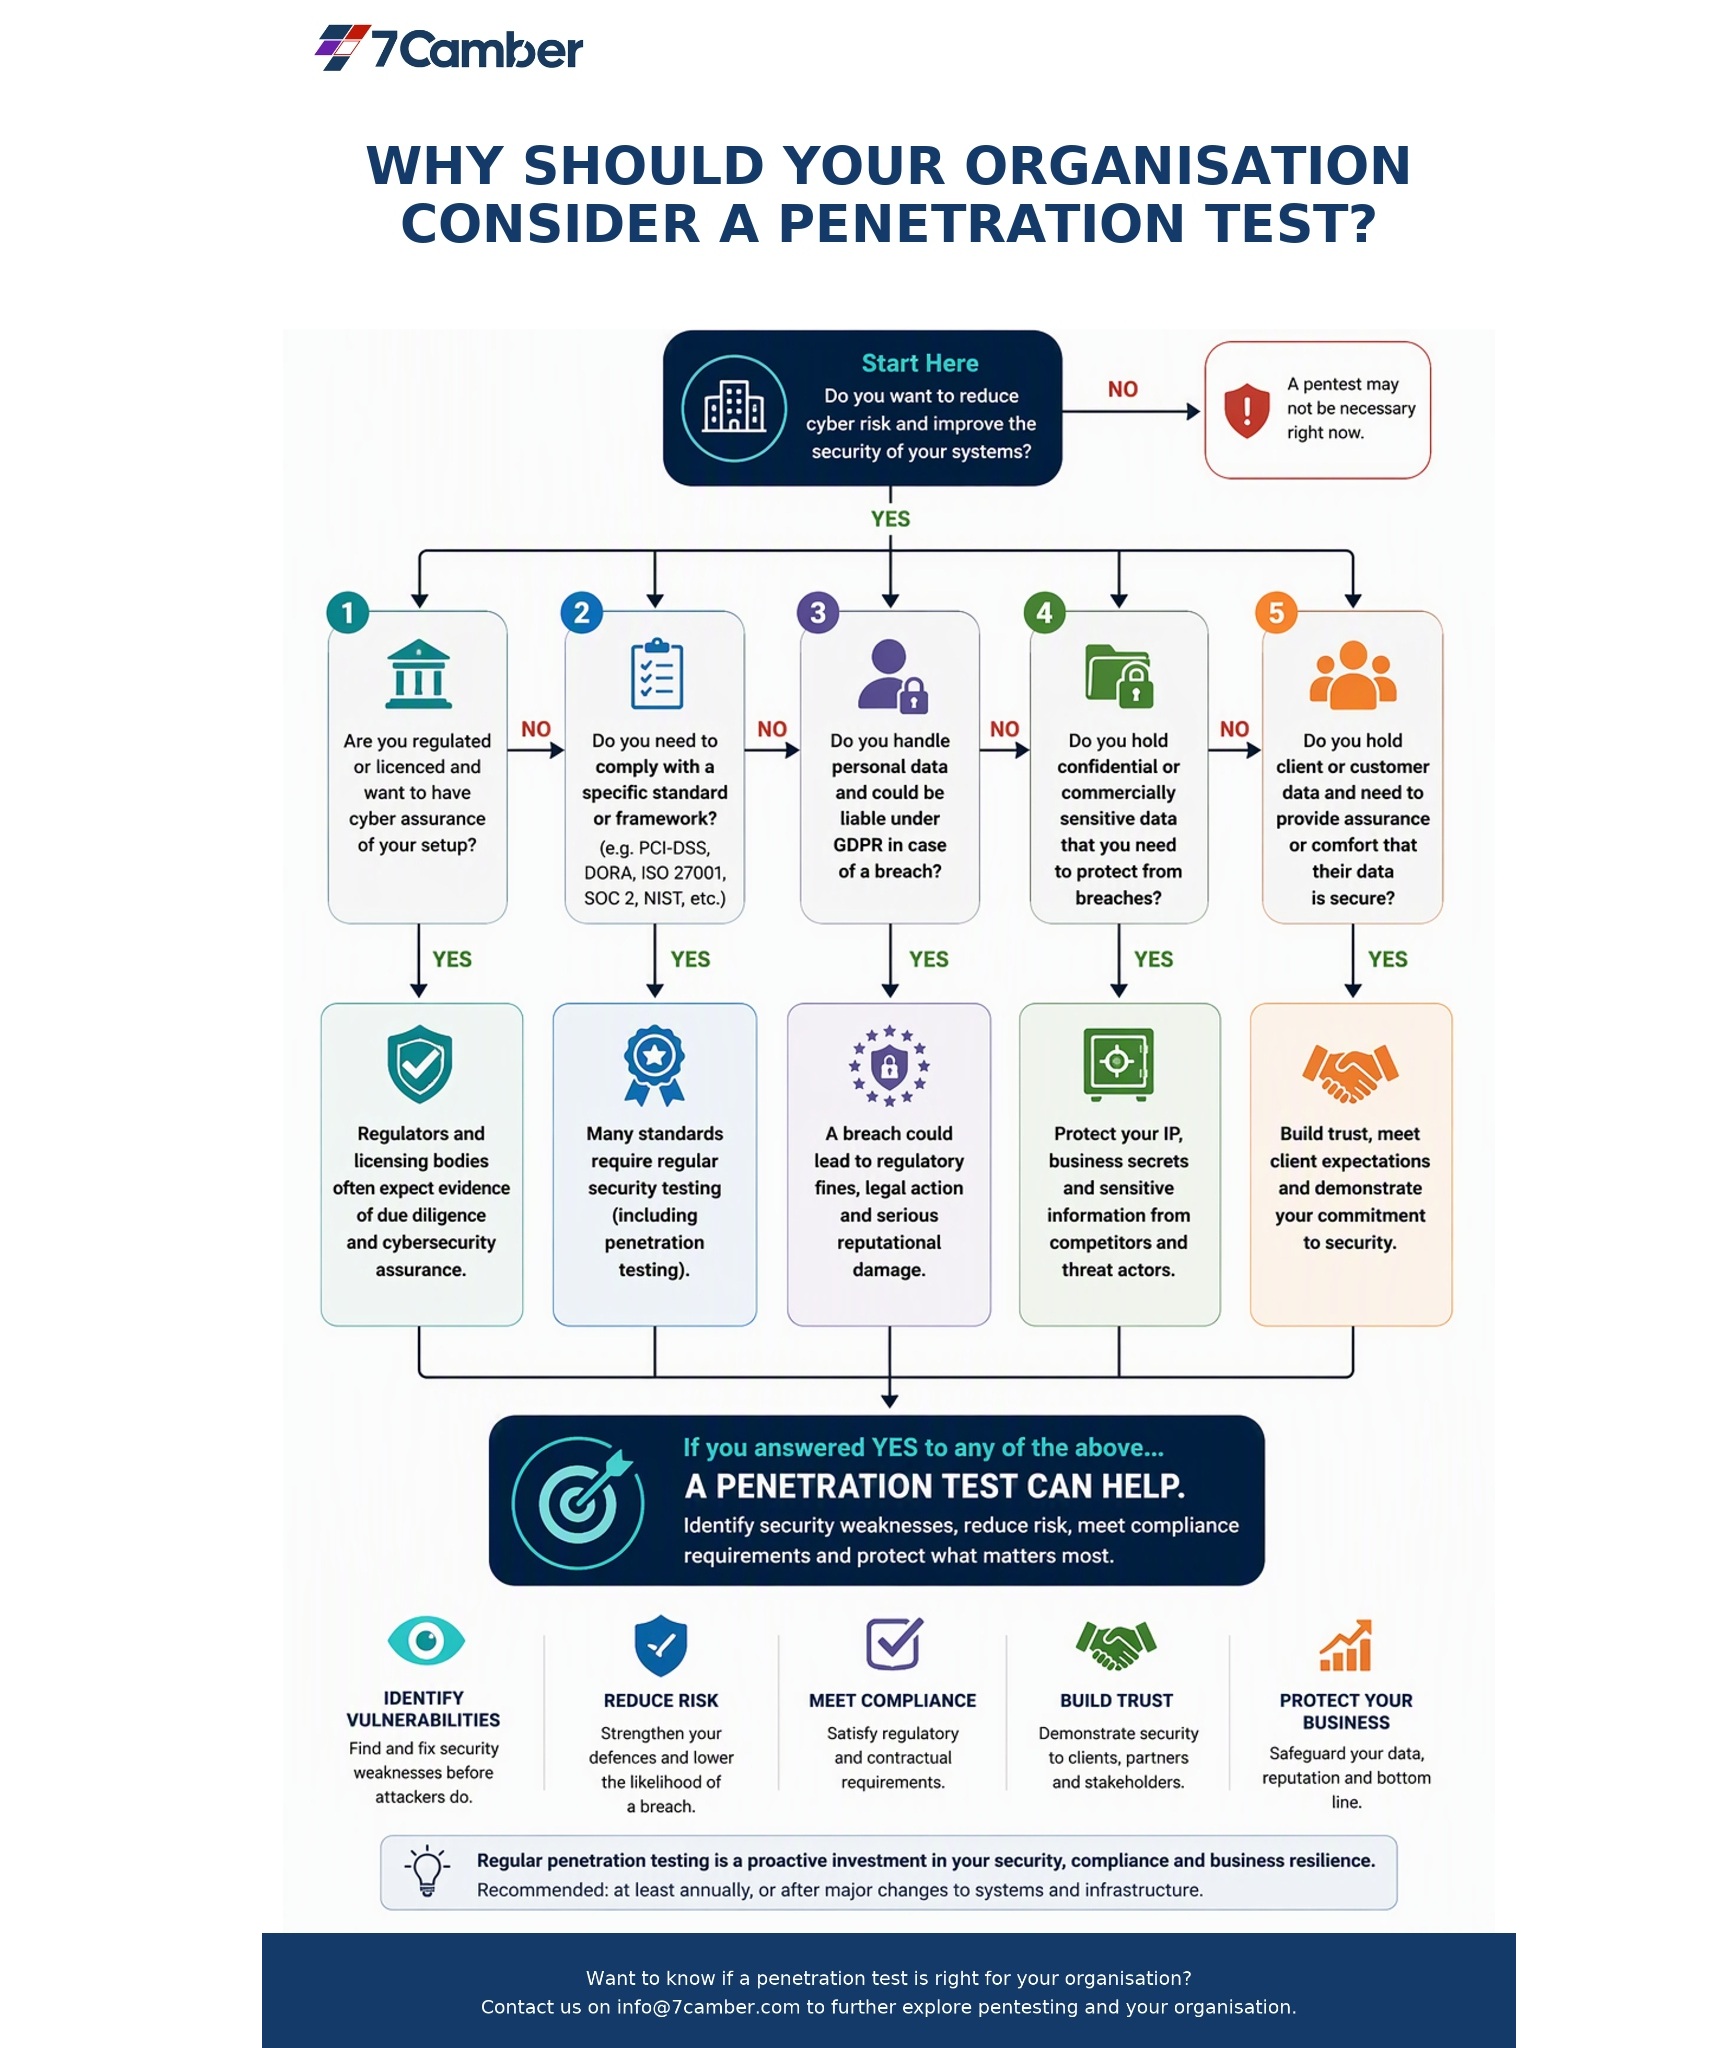
Why should I consider a penetration test?
If your organisation handles sensitive data, operates in a regulated industry, or wants to reduce cyber risk, a penetration test…
-
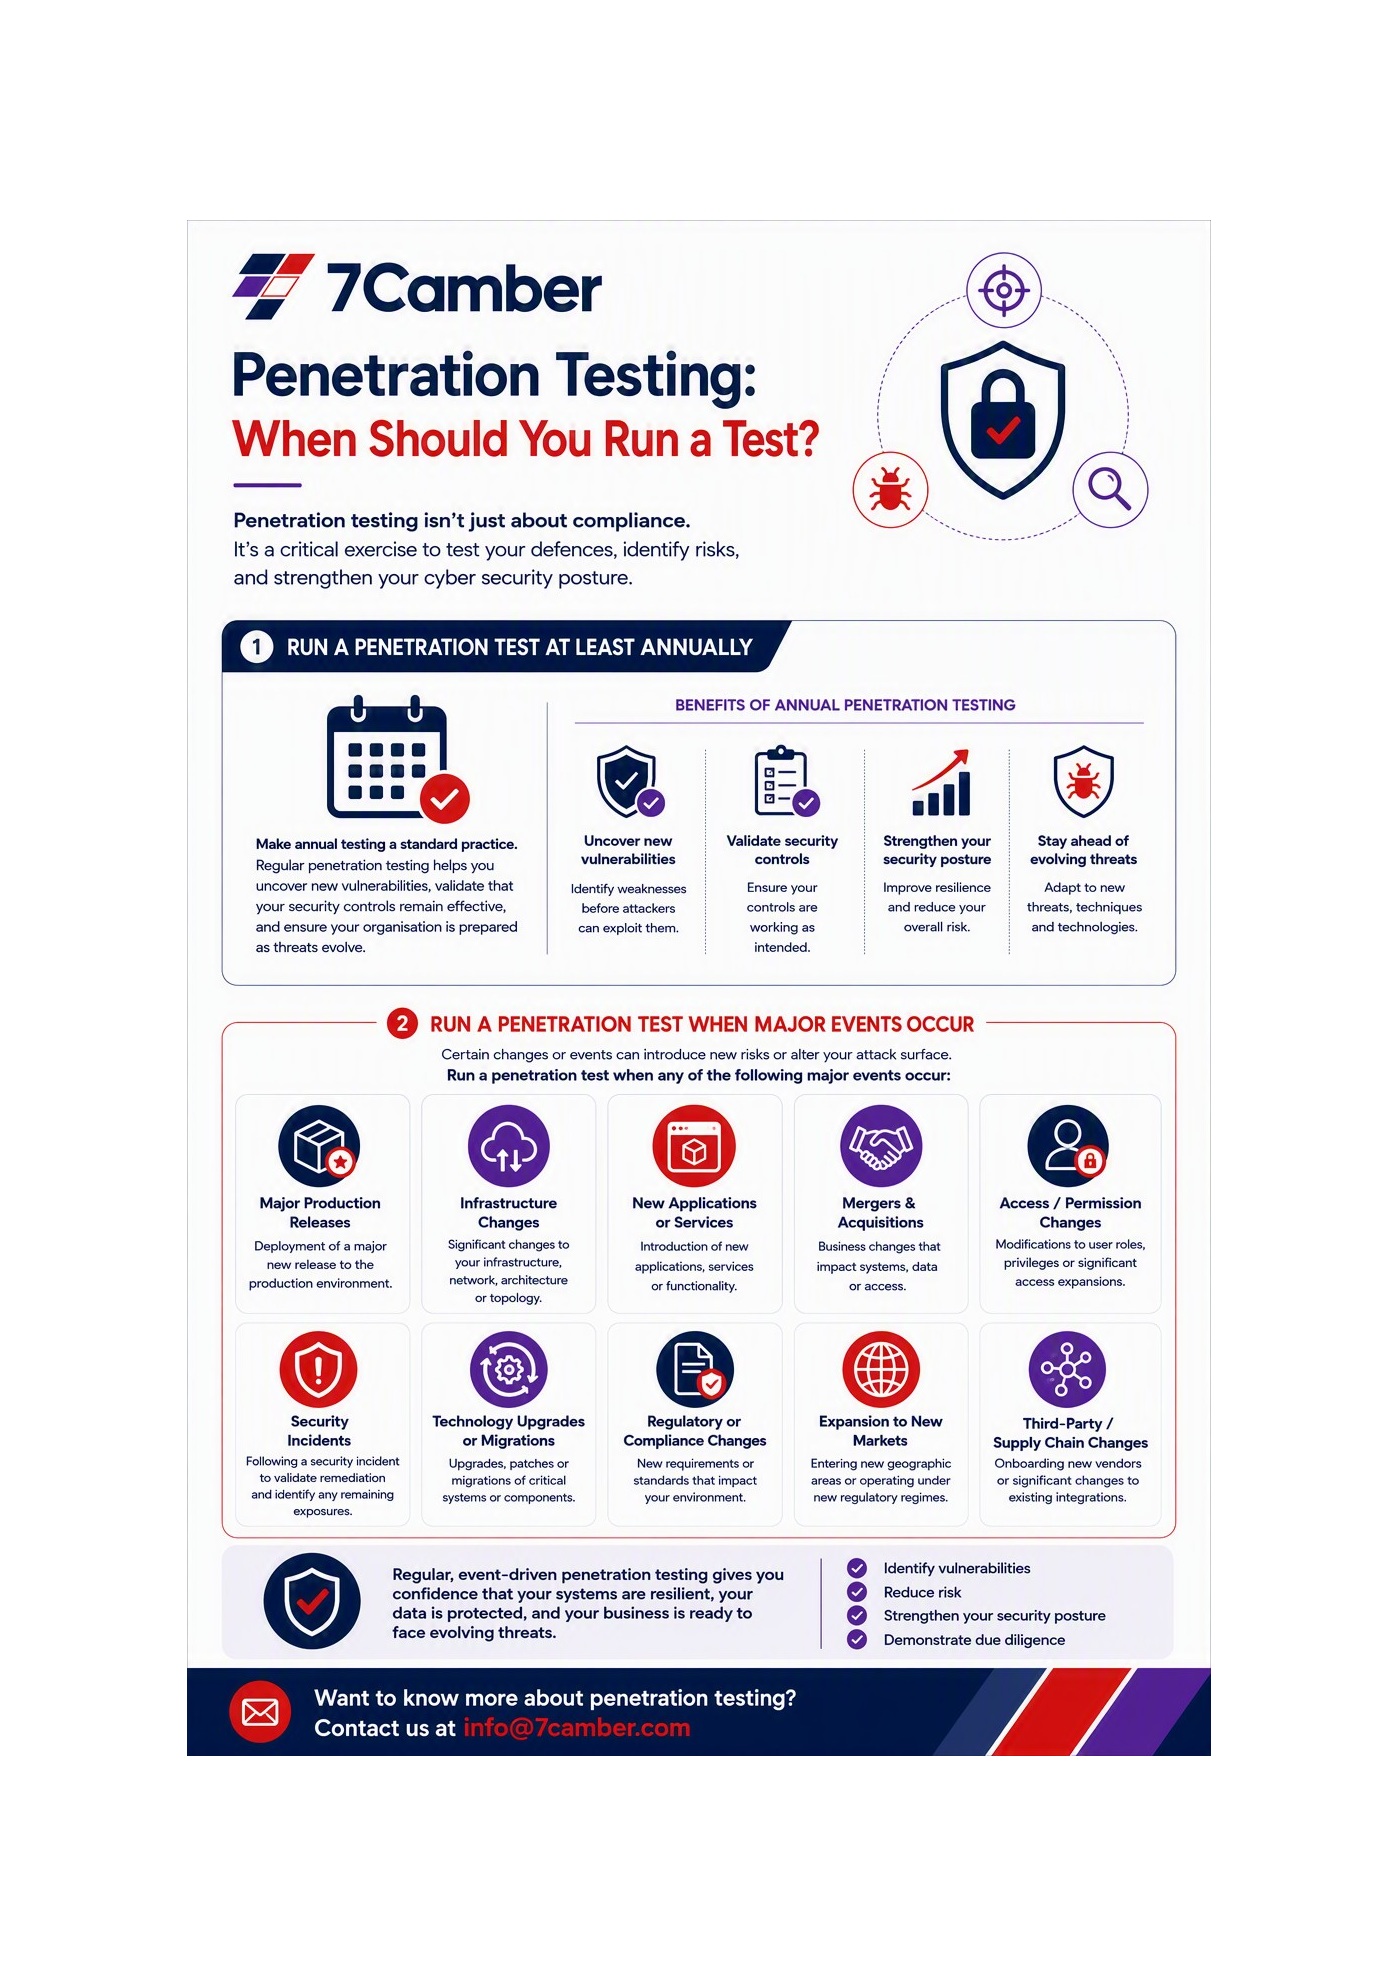
When Should You Run a Penetration Test? The Critical Moments Most Organisations Overlook
Many organisations only perform penetration tests to meet compliance requirements. However, the right time to run a penetration test is…
-
The Myth of Invisibility: Why “No Public-Facing Services” Is Not a Security Strategy
Having no public-facing systems doesn’t make your organisation secure. In today’s interconnected world, risk lies in access, identity, and internal…
-
7 Reasons Not to Carry Out a Penetration Test…and why they’re risky
Many organisations delay penetration testing for sensible‑sounding reasons. This post explores seven of the most common—and why they may do…